Srida IT · Audit · Assurance
Audit. Assure. Advance.
Technology-enabled audit & assurance for a changing digital world. Srida IT helps organisations understand risk, evaluate controls and strengthen digital trust through structured, evidence-based audit and assurance.
Evidence-based assessments
Risk-focused methodology
Technology-enabled delivery
Actionable recommendations
Continuous improvement
Audit & Assurance · our primary business
Independent, evidence-based assurance.
We assess your controls against recognised standards and give you a clear, evidence-based view of where you stand and what to improve. These are independent assessments and readiness engagements — not accredited certification or statutory audit.
Explore Audit & Assurance Services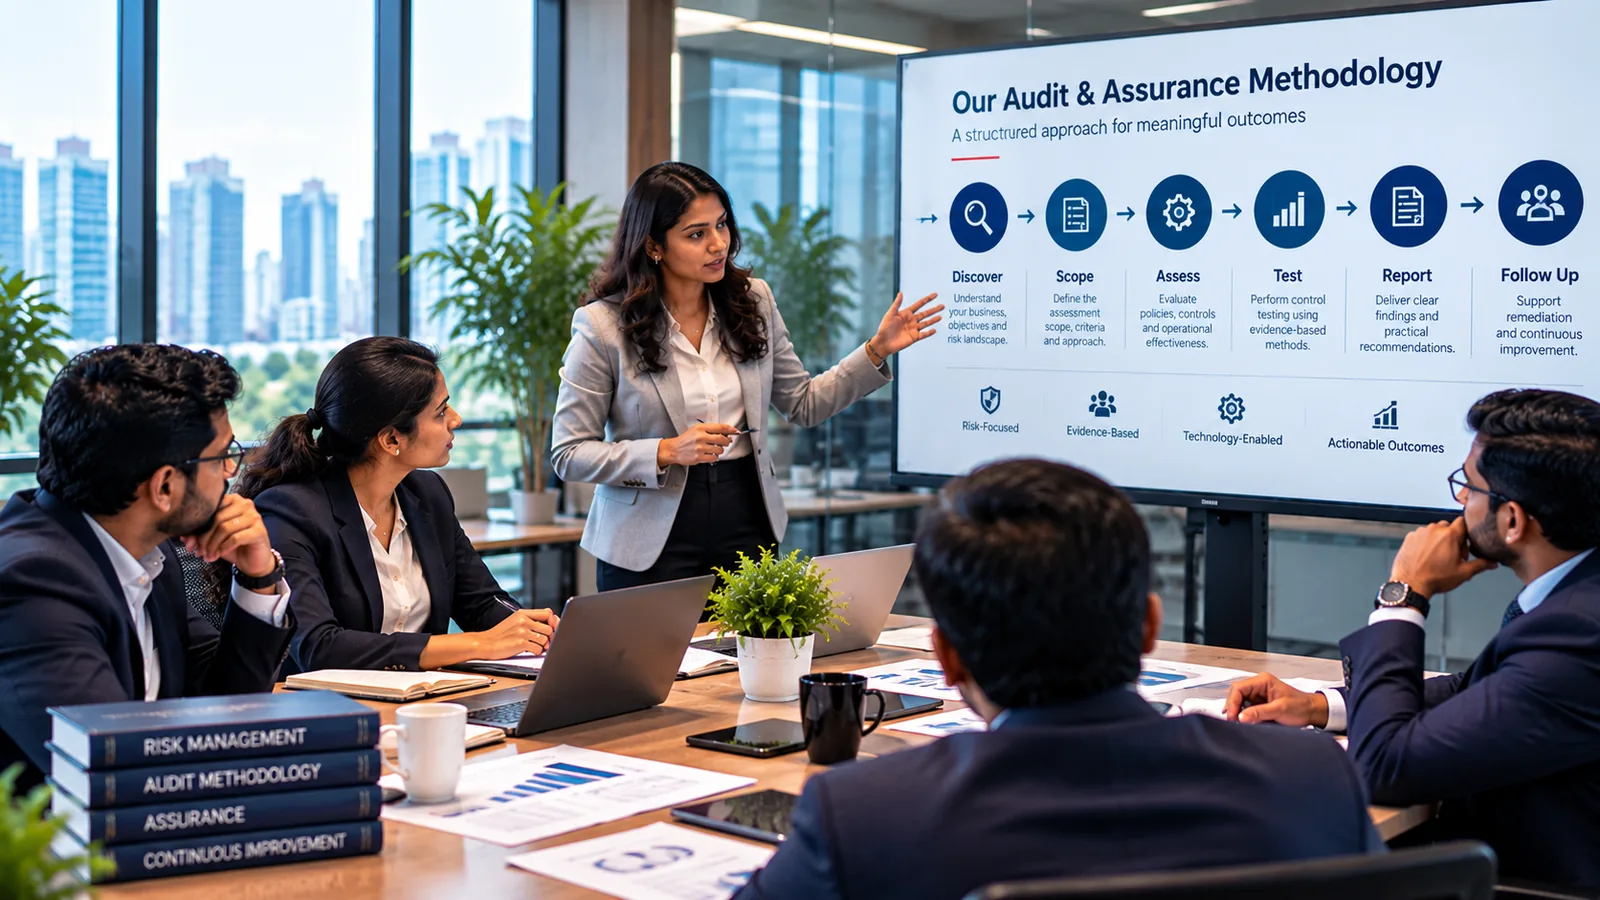
Cybersecurity & Information Security Audits
Independent assessment of your security posture against recognised standards.
IT Audit, ITGC & SOX Readiness
Evaluate IT general controls and prepare for ICFR/SOX requirements.
ISO Management System Internal Audits
Internal audits against ISO 27001, ISO 42001 and related standards.
AI Governance & AI Security Assessments
Assess AI risk, governance and security — NIST AI RMF, ISO 42001, EU AI Act.
Privacy & Regulatory Assessments
DPDPA and GDPR readiness, data-protection and consent assessments.
Cloud & Third-Party Assurance
Assess cloud security and the risk posture of vendors and partners.
Operational Resilience & OT Security
Business continuity, operational resilience and OT/ICS security reviews.
Continuous Control Monitoring & Assurance
Move from point-in-time audit to continuous, evidence-based assurance.
Why Srida IT
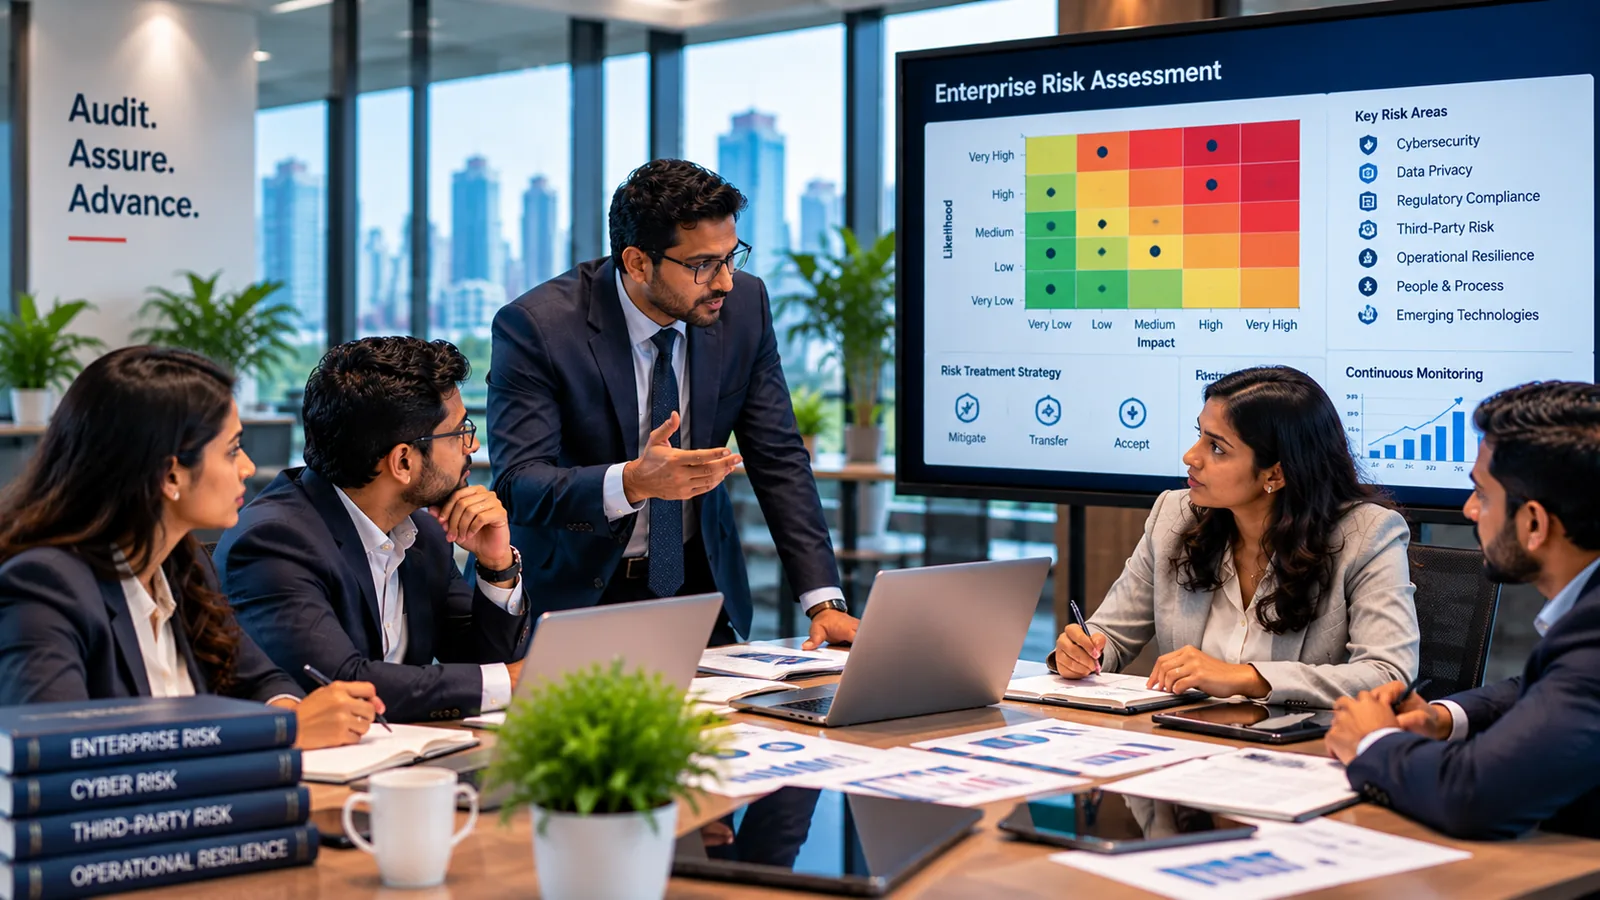
Findings you can act on.
- Risk-based approach — We focus effort where the real risk sits — not a checklist.
- Evidence-driven — Findings are grounded in tested evidence, not assertions.
- Practical control evaluation — We assess whether controls actually work in practice.
- Actionable findings — Clear, prioritised recommendations you can act on.
- Long-term improvement — Built toward continuous assurance, not a one-off report.
Our methodology
A structured approach, end to end.
- 01
Discover
Understand your business, objectives and risk landscape.
- 02
Scope
Define the assessment scope, criteria and approach.
- 03
Assess
Evaluate policies, controls and operational effectiveness.
- 04
Test
Perform control testing using evidence-based methods.
- 05
Report
Deliver clear findings and practical recommendations.
- 06
Follow Up
Support remediation and continuous improvement.
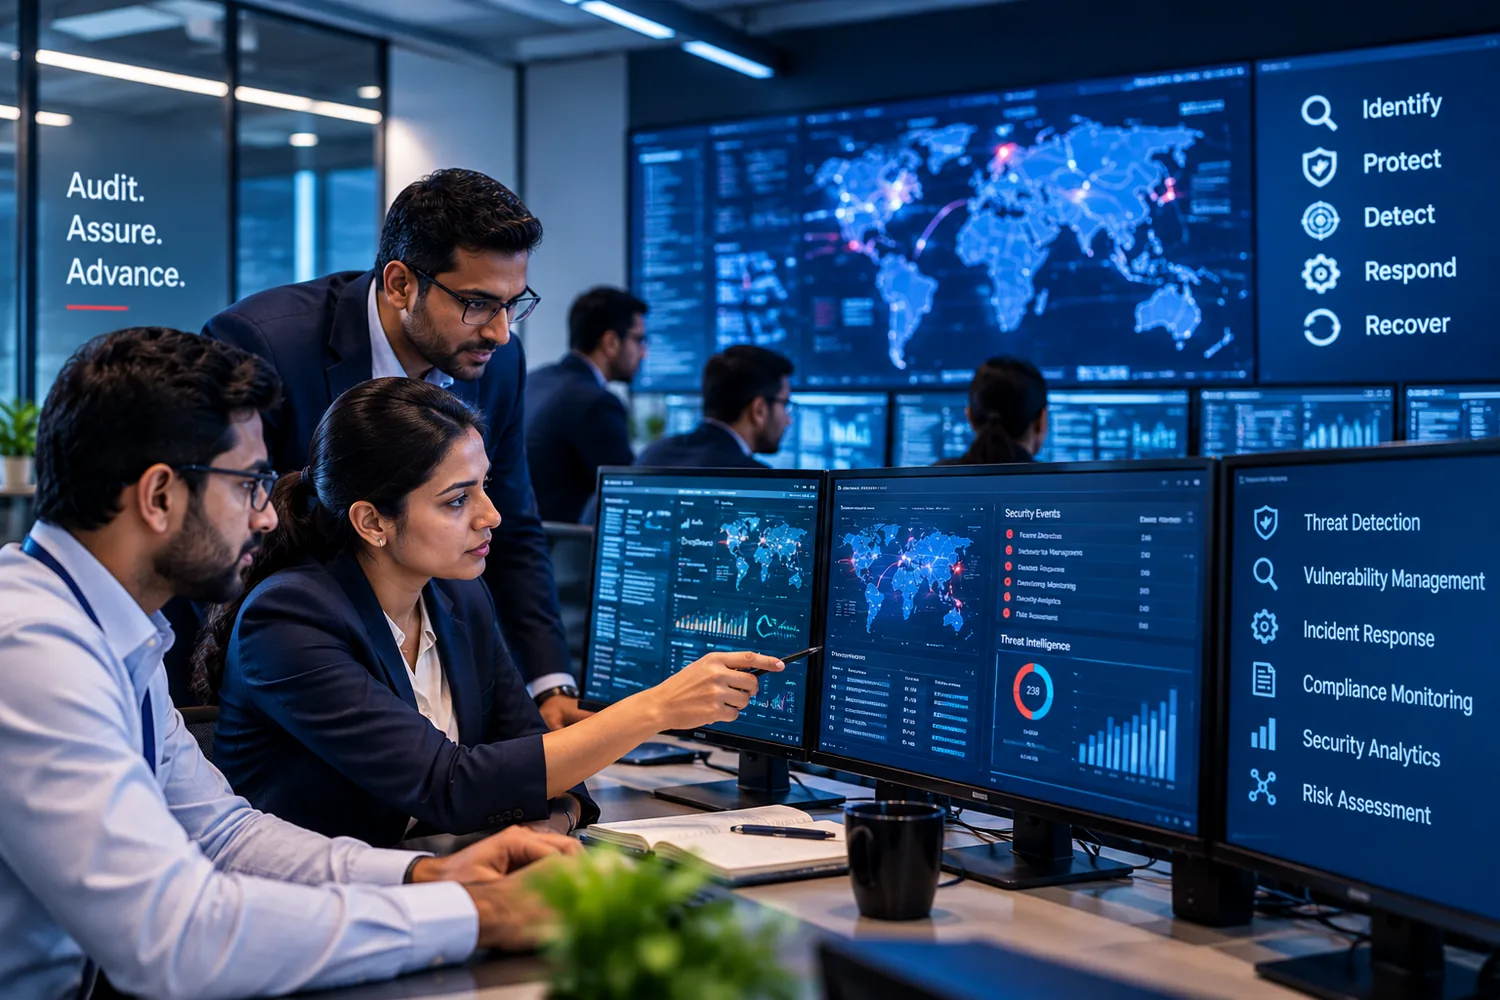
Spotlight · Cybersecurity assurance
Know where your security actually stands.
Independent cybersecurity and information-security assessments — mapped to recognised frameworks, grounded in tested evidence, and delivered as a clear, prioritised report.
Cybersecurity auditsTechnology Products
Purpose-built software for governance, risk & security.
Our products operationalise and accelerate assurance — turning point-in-time audit into continuous visibility for client teams.
Explore Technology Products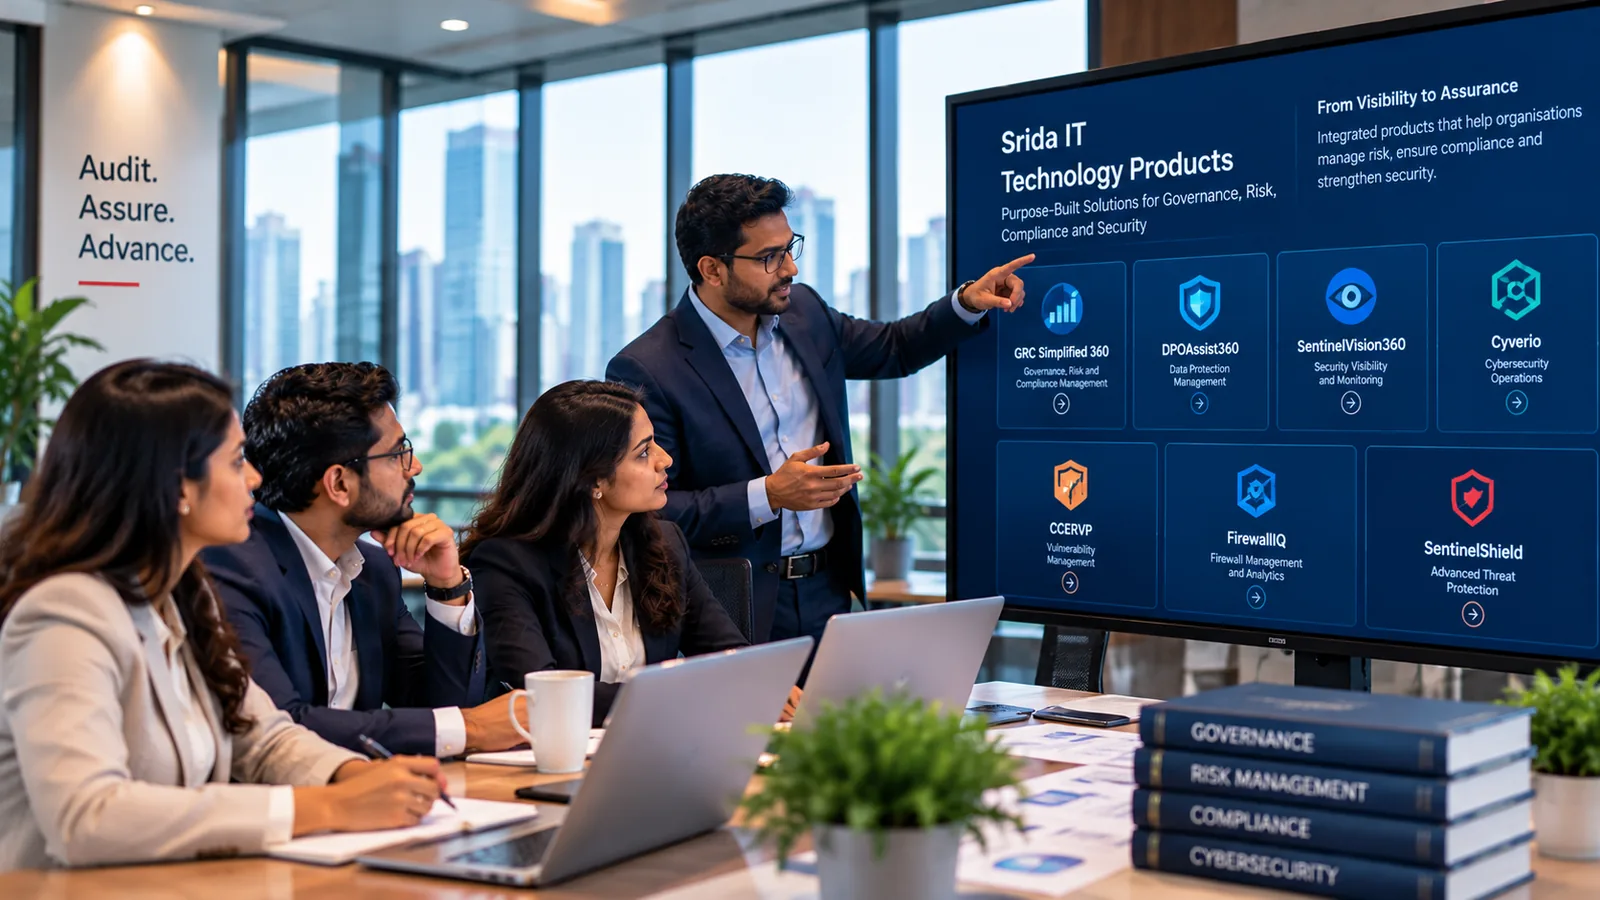
GRC Simplified 360
Unified governance, risk & compliance
DPOAssist360
Privacy operations for DPDPA, GDPR, CCPA
AI Exposure Auditor
Find your Shadow AI from existing logs
SentinelVision360
AI analytics on existing CCTV
Cyverio
Cybersecurity talent intelligence
FirewallIQ
Firewall audit & attack-path analysis
CCERVP
Control effectiveness validation
SentinelShield
Personal security agent (Android)
Spotlight · AI governance & security
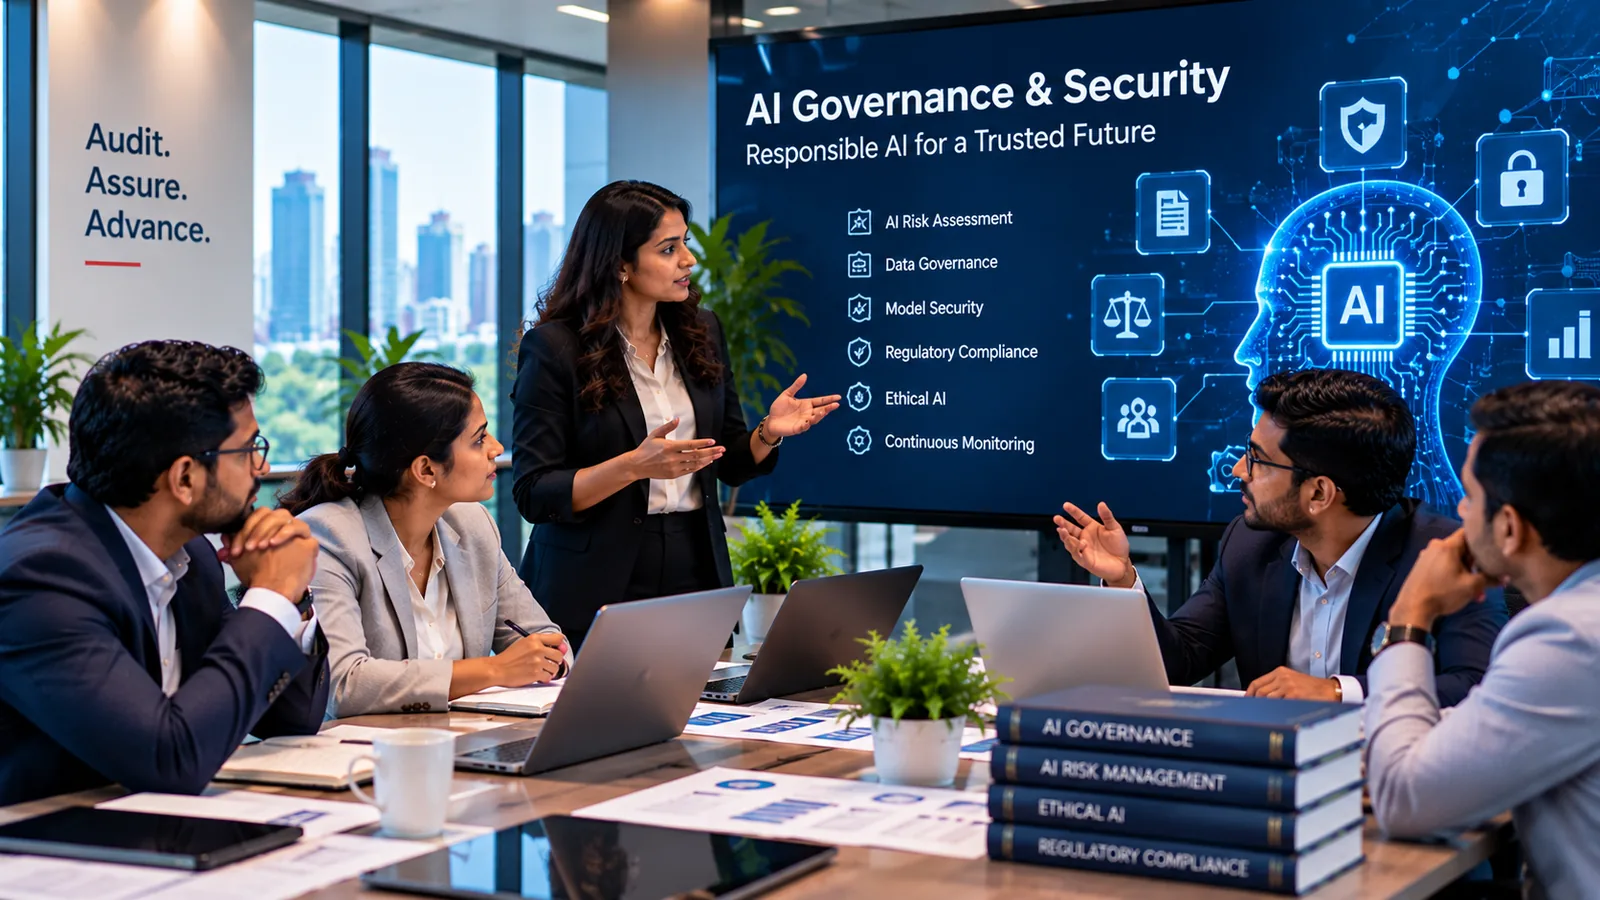
Govern AI before it governs you.
Assess AI risk, governance and security against NIST AI RMF, ISO 42001 and the EU AI Act — and discover the Shadow AI already running in your business with AI Exposure Auditor.
Frameworks & regulations
We assess against the standards, laws and control frameworks that matter to your business.
DPDPA · free readiness tool
India’s DPDP Act is here. Do you know where you stand?
5 minutes · Free · No login
Industries
Built for regulated industries.
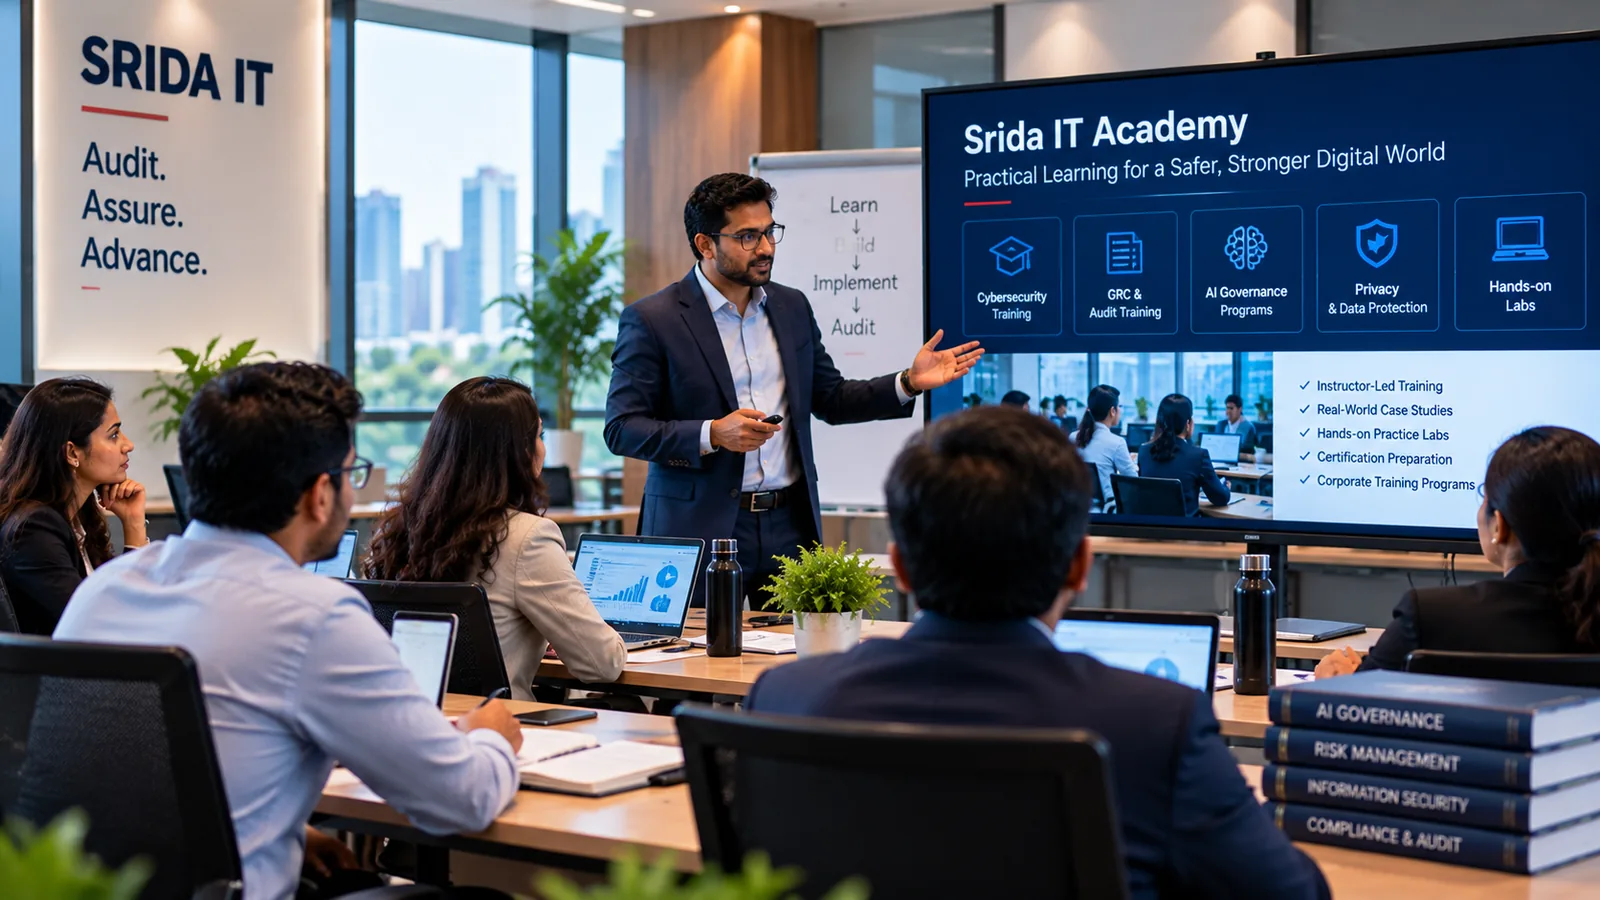
Srida IT Academy
Learn to apply it.
Practical, instructor-led training in audit, cybersecurity, GRC, privacy and AI governance — with hands-on labs, mentorship and internships.
Insights
Perspectives from the practice.
Audit. Assure. Advance.