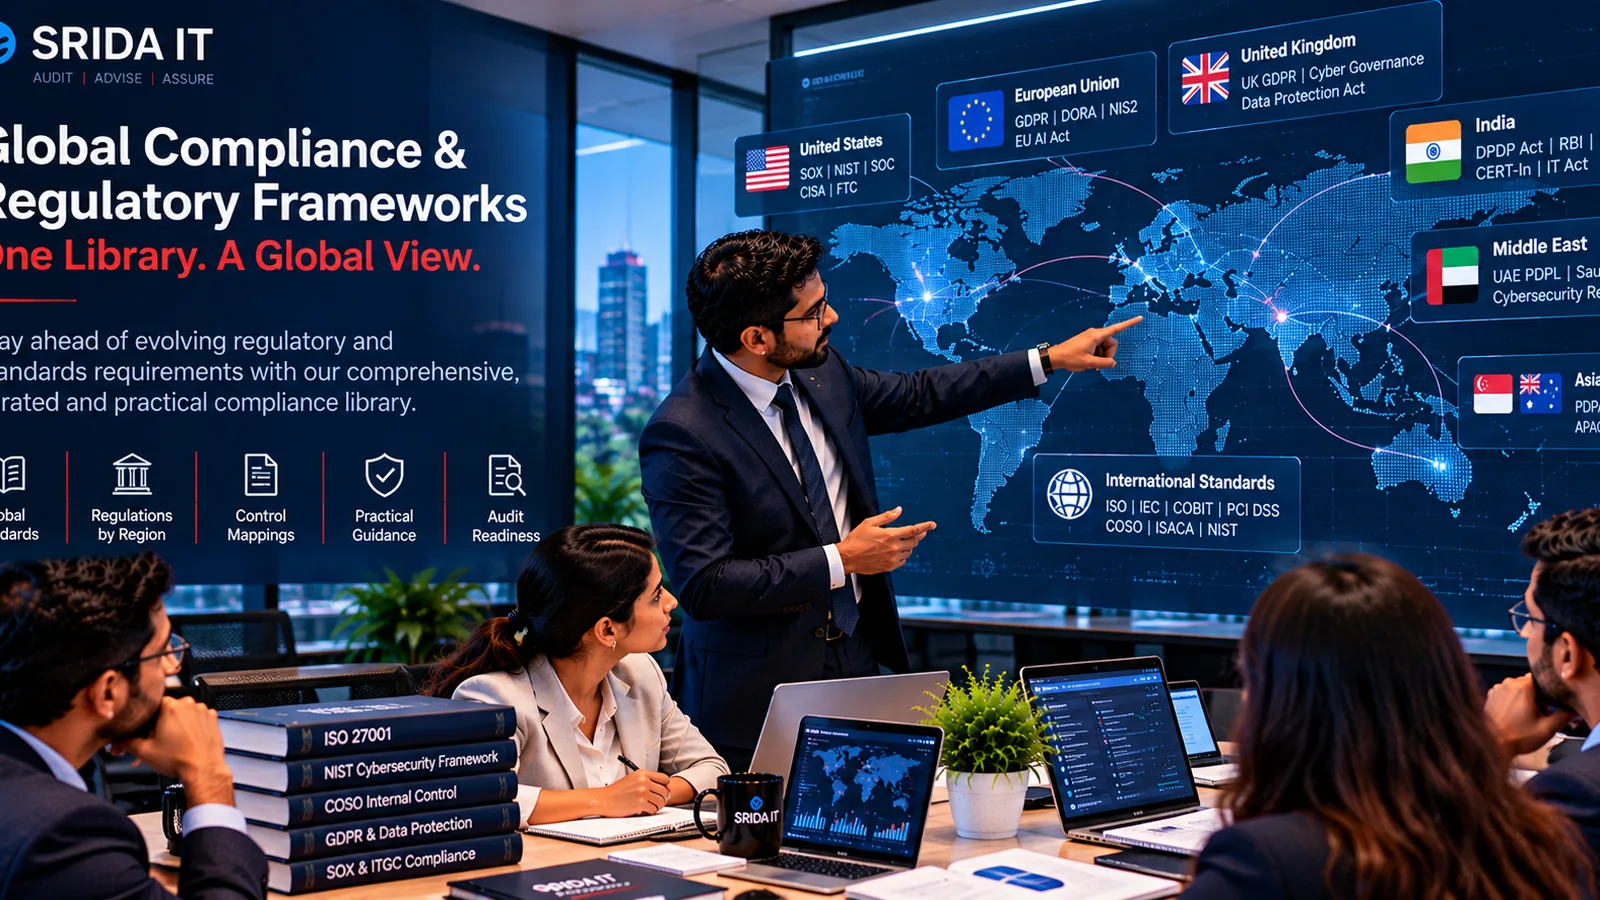
Global Compliance & Regulatory Framework Library
One library. A global view.
Understand the cybersecurity, privacy, IT governance, financial-control, AI-governance and resilience instruments that may apply to you — each classified by type, attributed to its issuing authority, dated, and linked to its official source. Information only, not legal advice.
Classified correctly
We distinguish legislation, regulations, directives, standards, control frameworks and assurance criteria — never a generic “regulation” label for everything.
Sourced & dated
Every entry links to its official source and shows when we last verified it. Volatile items carry a “verify current status” note.
Applicability-aware
We flag whether an instrument is mandatory, sector-specific, contractual, voluntary or conditional. It never implies everyone must comply with everything.
Search & filter
Find an instrument.
Showing 38 of 38 instruments. Results are an information aid, not a determination of legal applicability.
ISO 27001
InternationalISO/IEC 27001
Management system standard
ISO / IEC
Current edition: ISO/IEC 27001:2022
View details →ISO 42001
InternationalISO/IEC 42001
Management system standard
ISO / IEC
Current edition: ISO/IEC 42001:2023
View details →ISO 27701
InternationalISO/IEC 27701
Management system standard
ISO / IEC
Current edition: ISO/IEC 27701:2019 (extension to 27001)
View details →ISO 22301
InternationalManagement system standard
ISO
Current edition: ISO 22301:2019
View details →ISO 31000
InternationalVoluntary standard
ISO
Current edition: ISO 31000:2018 (guidance, not certifiable)
View details →NIST CSF
InternationalNIST Cybersecurity Framework
Control framework
US National Institute of Standards and Technology (NIST)
Current edition: CSF 2.0
View details →NIST AI RMF
InternationalNIST AI Risk Management Framework
Control framework
US National Institute of Standards and Technology (NIST)
AI RMF 1.0 (with Generative AI Profile companion)
View details →SP 800-53
InternationalNIST SP 800-53
Control framework
US National Institute of Standards and Technology (NIST)
Revision 5 (with ongoing release updates)
View details →CIS Controls
InternationalCIS Critical Security Controls
Control framework
Center for Internet Security (CIS)
CIS Controls v8.1
View details →COBIT
InternationalGovernance framework
ISACA
COBIT 2019
View details →COSO ICIF
InternationalCOSO Internal Control – Integrated Framework
Control framework
Committee of Sponsoring Organizations of the Treadway Commission (COSO)
2013 Framework
View details →PCI DSS
InternationalIndustry security standard
PCI Security Standards Council
Current version: 4.0.1
View details →SOC 2
InternationalAssurance / attestation criteria
AICPA (Trust Services Criteria; SSAE 18 attestation standards)
Trust Services Criteria (2017, revised 2022)
View details →SOC 1
InternationalAssurance / attestation criteria
AICPA (SSAE 18, AT-C 320)
SSAE 18 attestation standards
View details →DPDP Act
IndiaDigital Personal Data Protection Act, 2023
Legislation / Act
Parliament of India (administered by MeitY)
Enacted; commencement notified in phases
View details →DPDP Rules
IndiaDigital Personal Data Protection Rules, 2025
Regulation
Ministry of Electronics and Information Technology (MeitY)
Notified; phased commencement
View details →IT Act
IndiaInformation Technology Act, 2000
Legislation / Act
Parliament of India
In force (as amended, incl. 2008); various IT Rules made under it
Official source ↗CERT-In Directions
IndiaCERT-In Directions (April 2022)
Regulatory direction
Indian Computer Emergency Response Team (CERT-In), MeitY
In force
View details →RBI IT Governance MD
IndiaRBI Master Direction — IT Governance, Risk, Controls and Assurance Practices, 2023
Regulatory direction
Reserve Bank of India (RBI)
In force
View details →SEBI CSCRF
IndiaSEBI Cybersecurity and Cyber Resilience Framework
Regulatory direction
Securities and Exchange Board of India (SEBI)
In force (phased; deadlines extended)
View details →SOX
United StatesSarbanes–Oxley Act of 2002
Legislation / Act
US Congress (SEC/PCAOB oversight)
In force
View details →ITGC
United StatesIT General Controls
Control category
— (a category of controls, not a law or standard)
Control category used in audit and SOX/ICFR contexts
View details →SP 800-171
United StatesNIST SP 800-171
Control framework
US National Institute of Standards and Technology (NIST)
Revision 3
Official source ↗GDPR
European UnionGeneral Data Protection Regulation
Regulation
European Union (Regulation (EU) 2016/679)
In force
View details →DORA
European UnionDigital Operational Resilience Act
Regulation
European Union (Regulation (EU) 2022/2554)
In force / applies
View details →NIS2
European UnionNIS2 Directive
Directive
European Union (Directive (EU) 2022/2555)
In force; transposed into national law (dates vary by member state)
View details →EU AI Act
European UnionEU Artificial Intelligence Act
Regulation
European Union (Regulation (EU) 2024/1689)
In force; obligations apply in phases
View details →UK GDPR / DPA 2018
United KingdomUK GDPR & Data Protection Act 2018
Legislation / Act
UK Parliament; Information Commissioner's Office (ICO)
In force (as amended by the DUAA 2025)
Official source ↗DUAA 2025
United KingdomData (Use and Access) Act 2025
Legislation / Act
UK Parliament
Enacted; provisions commencing in stages
View details →Cyber Essentials
United KingdomCyber Essentials / Cyber Essentials Plus
Voluntary standard
UK National Cyber Security Centre (NCSC), delivered by IASME
Current scheme
Official source ↗UAE PDPL
Middle EastUAE Personal Data Protection Law
Legislation / Act
UAE (Federal Decree-Law No. 45 of 2021); UAE Data Office
In force; federal Executive Regulations still pending
View details →Saudi PDPL
Middle EastSaudi Personal Data Protection Law
Legislation / Act
Kingdom of Saudi Arabia (Royal Decree M/19, amended M/148); SDAIA
In force and enforceable
View details →NCA ECC
Middle EastNCA Essential Cybersecurity Controls
Regulatory direction
Saudi National Cybersecurity Authority (NCA)
In force (ECC and related NCA frameworks)
Official source ↗Singapore PDPA
Asia-PacificSingapore Personal Data Protection Act
Legislation / Act
Personal Data Protection Commission (PDPC), Singapore
In force (amended)
Official source ↗SG Cybersecurity Act
Asia-PacificSingapore Cybersecurity Act (as amended 2024)
Legislation / Act
Cyber Security Agency of Singapore (CSA)
In force; amended 2024
View details →Privacy Act 1988
Asia-PacificAustralia Privacy Act 1988 (as reformed 2024)
Legislation / Act
Office of the Australian Information Commissioner (OAIC)
In force; reformed by the Privacy and Other Legislation Amendment Act 2024
View details →Essential Eight
Asia-PacificACSC Essential Eight
Maturity model
Australian Signals Directorate / Australian Cyber Security Centre (ACSC)
Current (Maturity Model updated periodically)
Official source ↗APPI
Asia-PacificJapan Act on the Protection of Personal Information
Legislation / Act
Personal Information Protection Commission (PPC), Japan
In force (amended)
Official source ↗By jurisdiction
Regulations by region, country by country.
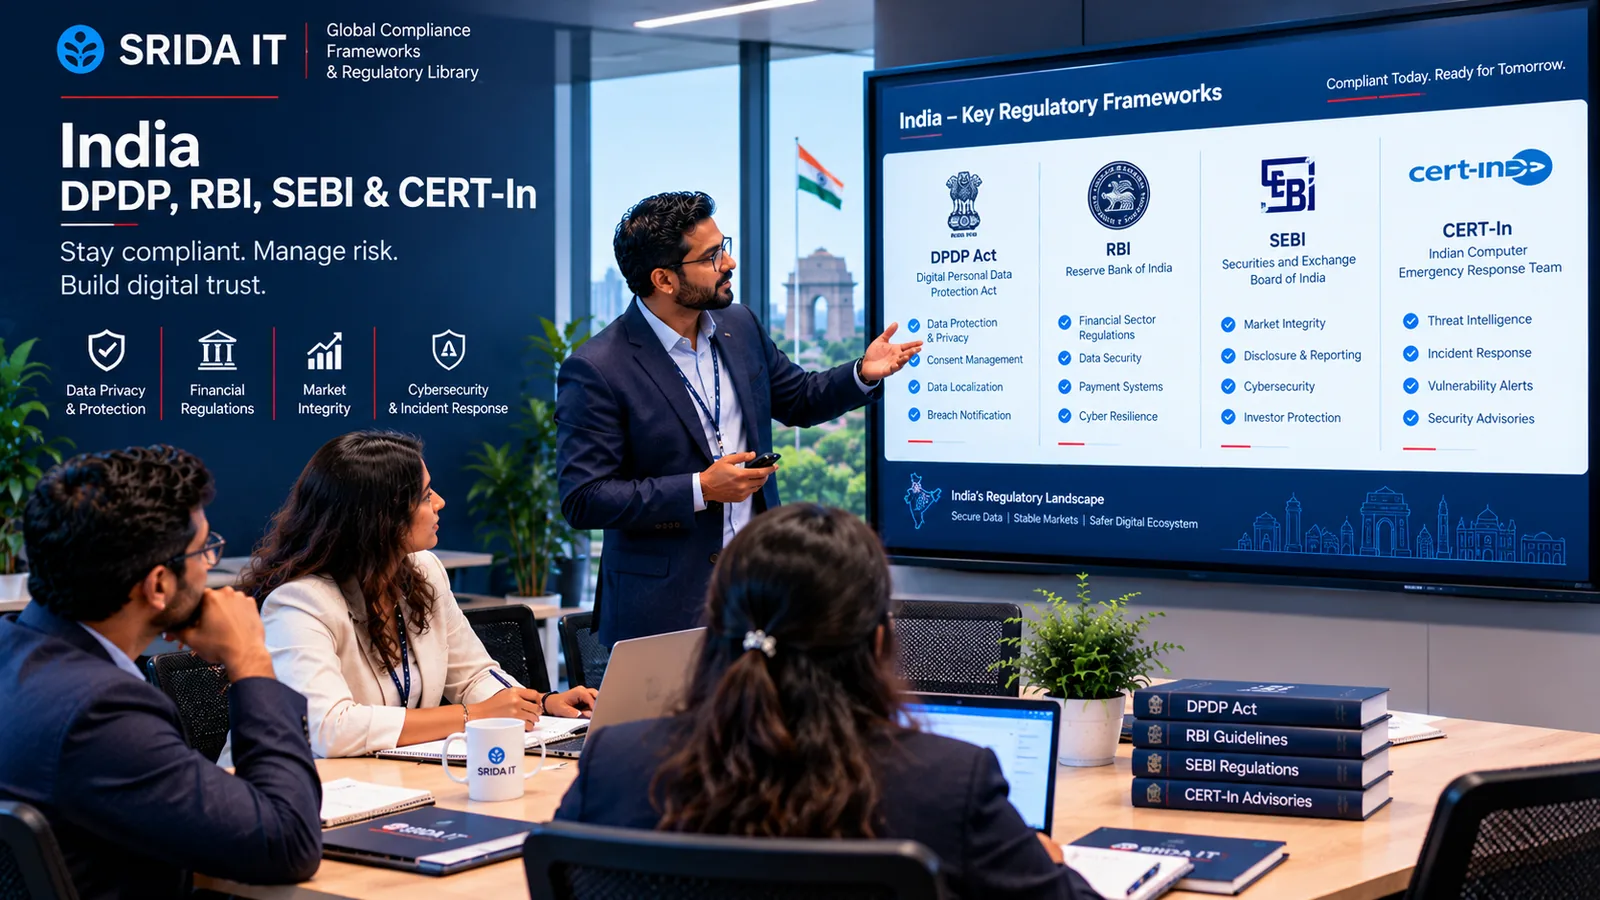
India
DPDP Act & Rules, IT Act, CERT-In, RBI and SEBI requirements.
View India →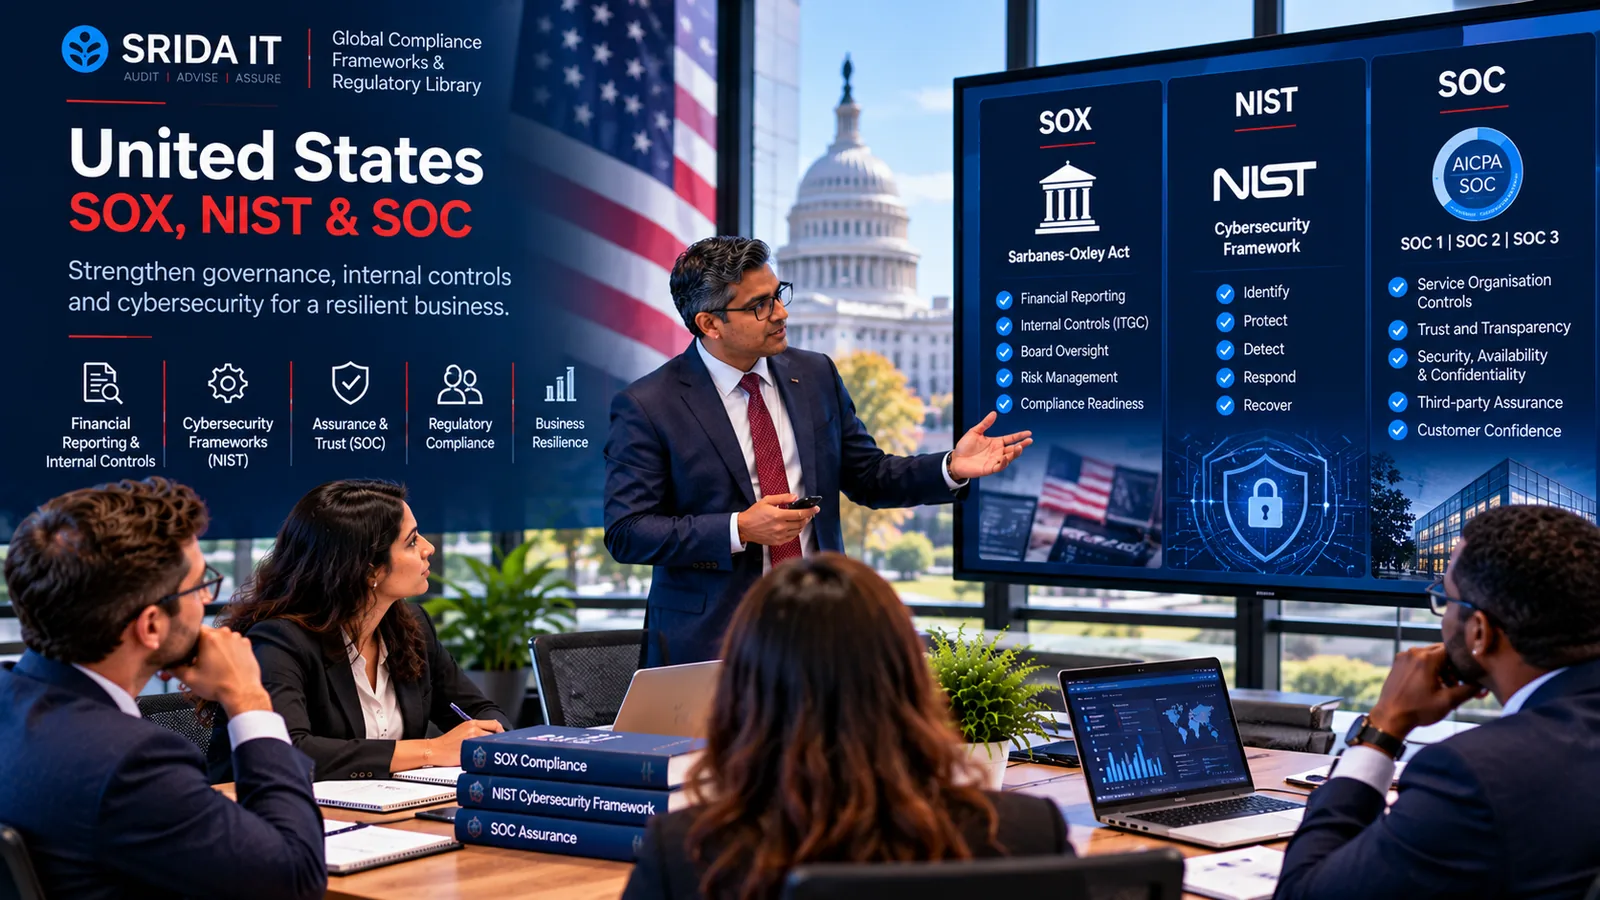
United States
SOX, COSO, the NIST family and SOC reporting.
View United States →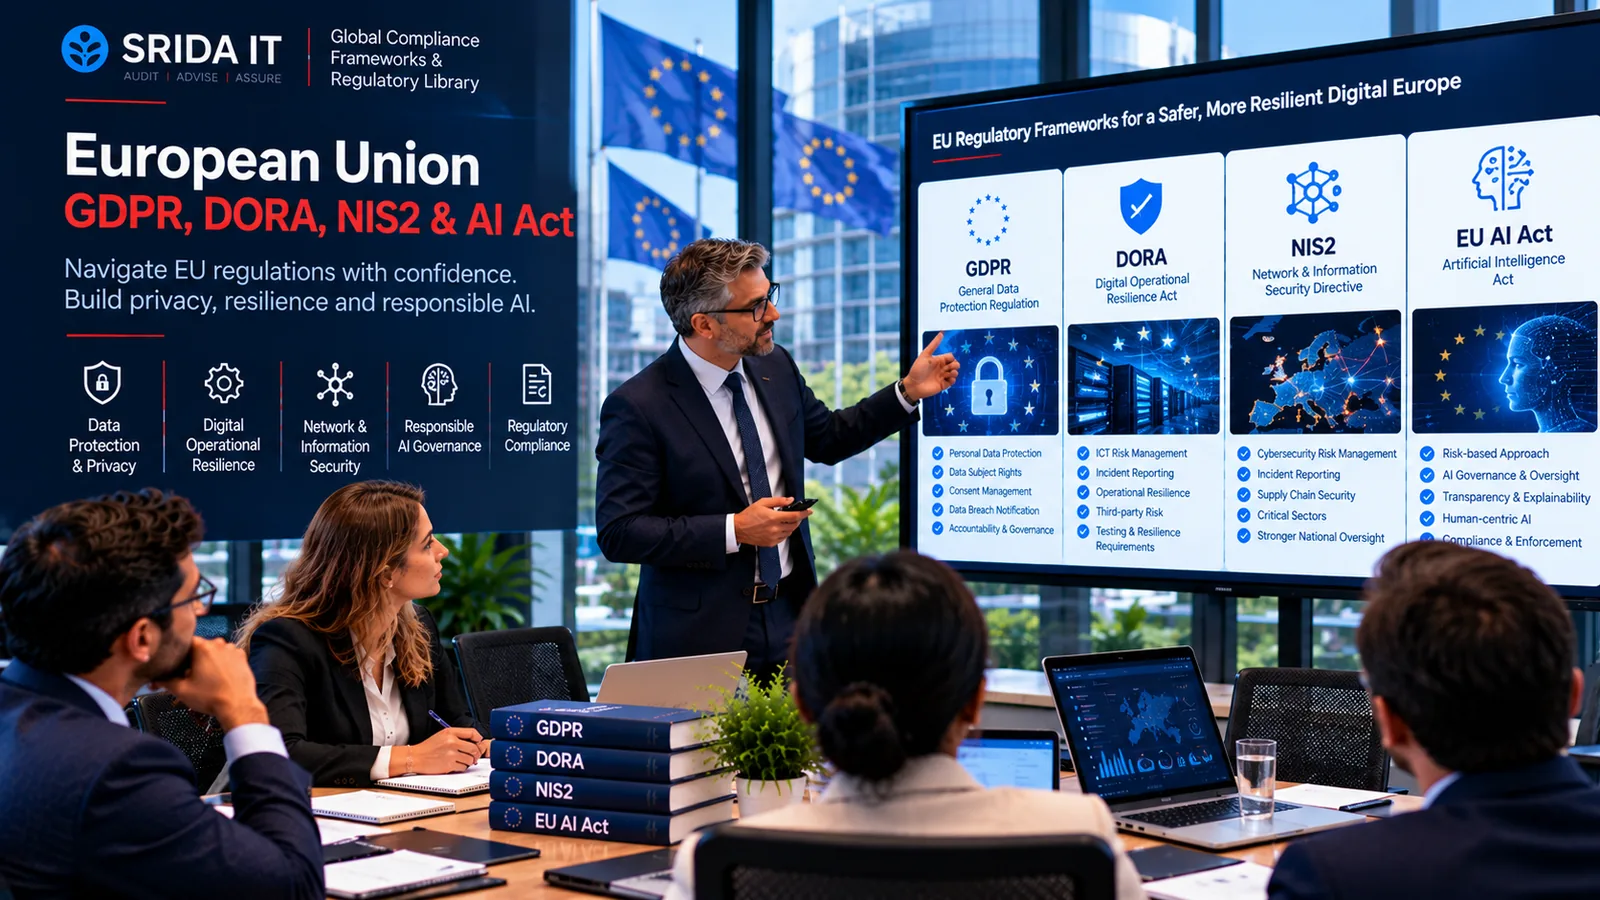
European Union
GDPR, DORA, NIS2 and the EU AI Act.
View European Union →
United Kingdom
UK GDPR, DPA 2018, the DUAA 2025, NIS and Cyber Essentials.
View United Kingdom →
Middle East
UAE and Saudi Arabia data-protection and cybersecurity.
View Middle East →
Asia-Pacific
Singapore, Australia and Japan.
View Asia-Pacific →
International Standards
ISO/IEC, NIST, COBIT, COSO, CIS, PCI DSS and SOC.
View International Standards →Cross-framework view
Common control domains.
Governance
Risk assessment
Access control
Incident response
Business continuity
Supplier management
Privacy
AI governance
Audit evidence
Illustrative only. These groupings show instruments that address a similar subject area. They are not a claim of legal or clause-to-clause equivalence. Mapping one framework’s control to another requires an instrument-specific assessment, which we document with its basis during an engagement.
International standards
ISO/IEC, NIST, COBIT, COSO, CIS, PCI DSS and SOC.
The globally recognised standards and frameworks that underpin most assurance work — each with its current edition, issuing body and official reference.
View international standardsFramework implementation guides
Deep-dive guides.
In-depth Srida IT guides for the frameworks we implement and assess most often.
ISO Management Standards
International standards for information security, privacy, business continuity, and IT service management.
Privacy Regulations
Global data protection and privacy regulations governing personal data processing.
Security Standards
Technical security standards for payment card data, federal systems, and vulnerability testing.
Audit & Attestation
Independent audit frameworks for financial reporting, trust services, and IT controls.
This library provides general information for orientation only. It is not legal advice, a determination of applicability, or a substitute for formal certification or professional counsel. Verify current legal status, editions and dates against the official source before relying on any entry. Inclusion of a jurisdiction or instrument here is informational and does not imply that Srida IT provides regulated services, holds local authorisation, or has a presence in that jurisdiction.
Know the framework. Now prove you meet it.
Srida IT delivers independent, evidence-based assessments against these frameworks — worldwide.