Resilience · Audit & Assurance
Specialist · On requestResilience you can prove, not just plans on a shelf
Be ready to keep running when something goes wrong.
Continuity plans that have never been tested fail when they are needed most. We assess your business impact analysis, continuity and disaster-recovery readiness, and the exercises behind them — against ISO 22301 — so you know your organisation can actually keep running through disruption.
Who this is for
Built for the people who answer for it.
Operations & risk leaders
Accountable for keeping critical services running through disruption.
Regulated organisations
With operational-resilience obligations to evidence to regulators and customers.
Organisations after an incident
That learned the hard way their continuity plans were untested or incomplete.
Business risks addressed
What this assessment helps you find.
- Continuity plans that exist but have never been tested end-to-end.
- Recovery objectives (RTO/RPO) that the technology cannot actually meet.
- Critical dependencies and single points of failure that are undocumented.
- A plan that does not reflect the current business, people or technology.
- Inability to evidence resilience when a regulator or customer asks.
Assessment objectives
What the engagement evaluates.
- Assess the business impact analysis and recovery priorities.
- Evaluate continuity and disaster-recovery plans and their readiness.
- Review recovery exercises and their outcomes.
- Assess operational resilience of critical services end-to-end.
- Identify gaps against ISO 22301 and resilience good practice.
Scope & control areas
What we review.
Impact & priorities
- Business impact analysis (BIA)
- Critical process identification
- RTO / RPO definition
- Dependency mapping
Plans & recovery
- Business continuity plans
- Disaster recovery readiness
- Crisis management and communication
- Third-party and supply continuity
Testing & resilience
- Exercise and test review
- Lessons-learned and improvement
- Operational resilience of critical services
- Governance and ownership
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
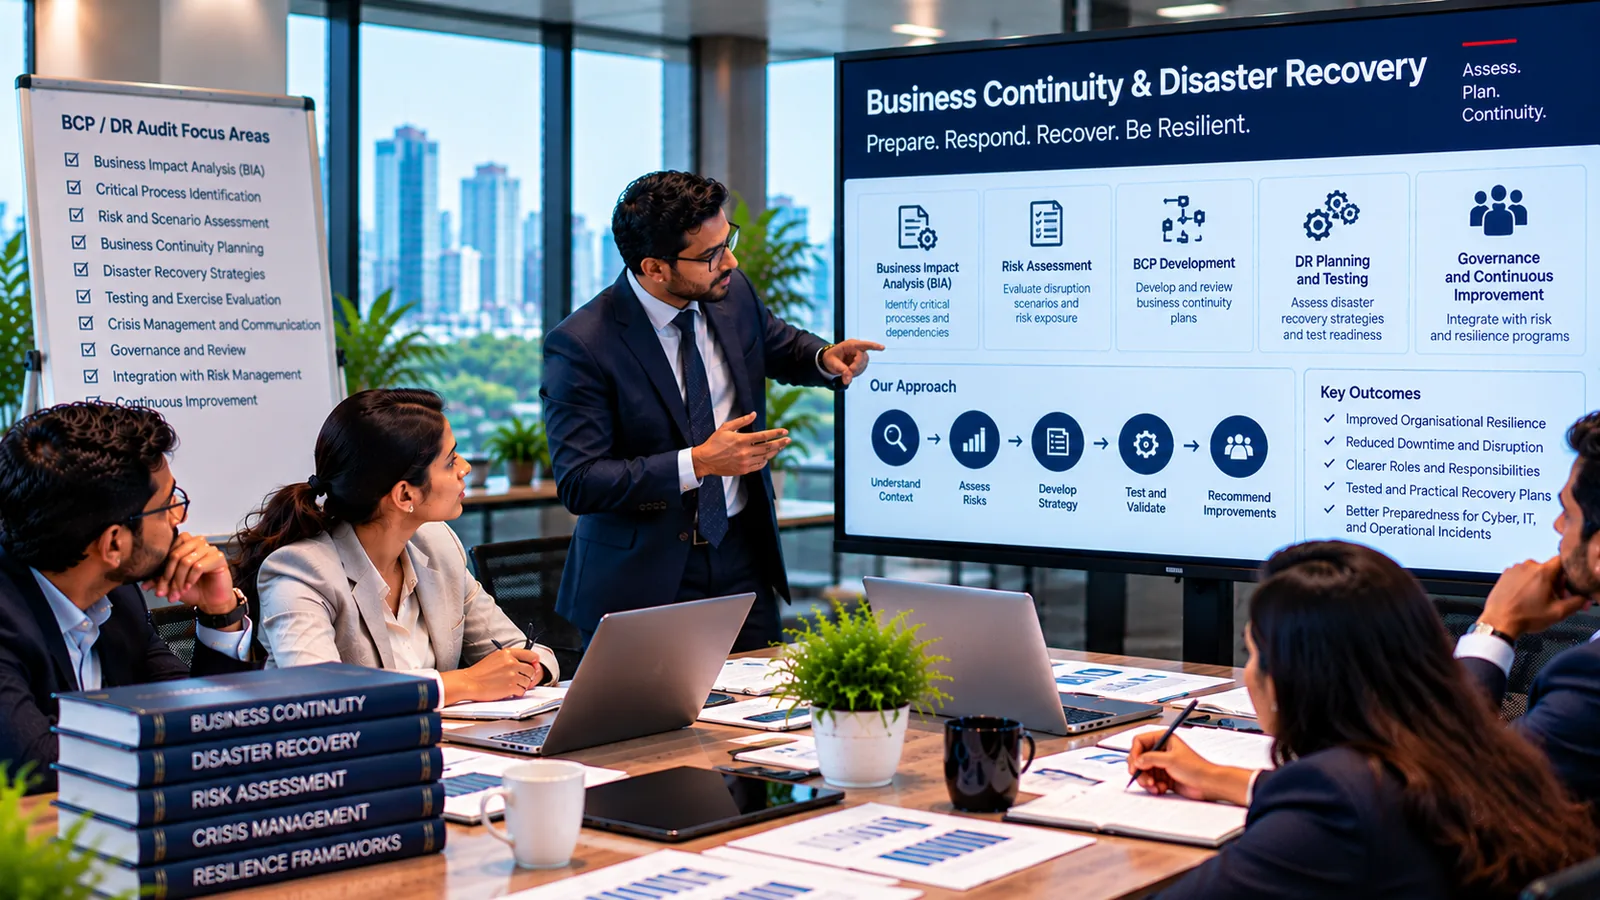
Our approach
A practical, evidence-based method.
Understand the business
Identify critical services, dependencies and the impact of disruption.
Review the BIA
Assess the business impact analysis and the recovery priorities and objectives it drives.
Assess plans
Evaluate continuity and disaster-recovery plans for completeness, currency and feasibility.
Review exercises
Assess how plans are tested and whether lessons are captured and acted upon.
Evaluate resilience
Assess end-to-end resilience of critical services, including third-party dependencies.
Report & improve
Deliver findings against ISO 22301 and a prioritised improvement roadmap.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- Business impact analysis and recovery objectives
- Business continuity and DR plans
- Exercise and test records
- Critical dependency and third-party maps
- Incident history and lessons learned
- Governance and ownership records
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- BIA and recovery-priority review
- Continuity and DR readiness assessment
- Exercise and testing review
- Operational-resilience assessment of critical services
- Gap analysis against ISO 22301
- Prioritised resilience improvement roadmap
Engagement options
Engage the way that fits.
Readiness assessment
A review of continuity and DR readiness against ISO 22301.
Exercise review
An independent review of a continuity or DR exercise and its outcomes.
Resilience programme review
An end-to-end assessment of operational resilience for critical services.
Independence & scope of this service
This is a specialist engagement scoped on request. It is an independent readiness and resilience assessment aligned to ISO 22301 — not accredited certification. We assess and recommend; executing recovery or invoking plans remains your organisation's responsibility.
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your business continuity & resilience engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.