Cloud & Supply Chain · Audit & Assurance
AvailableYour risk now lives in your cloud and your vendors
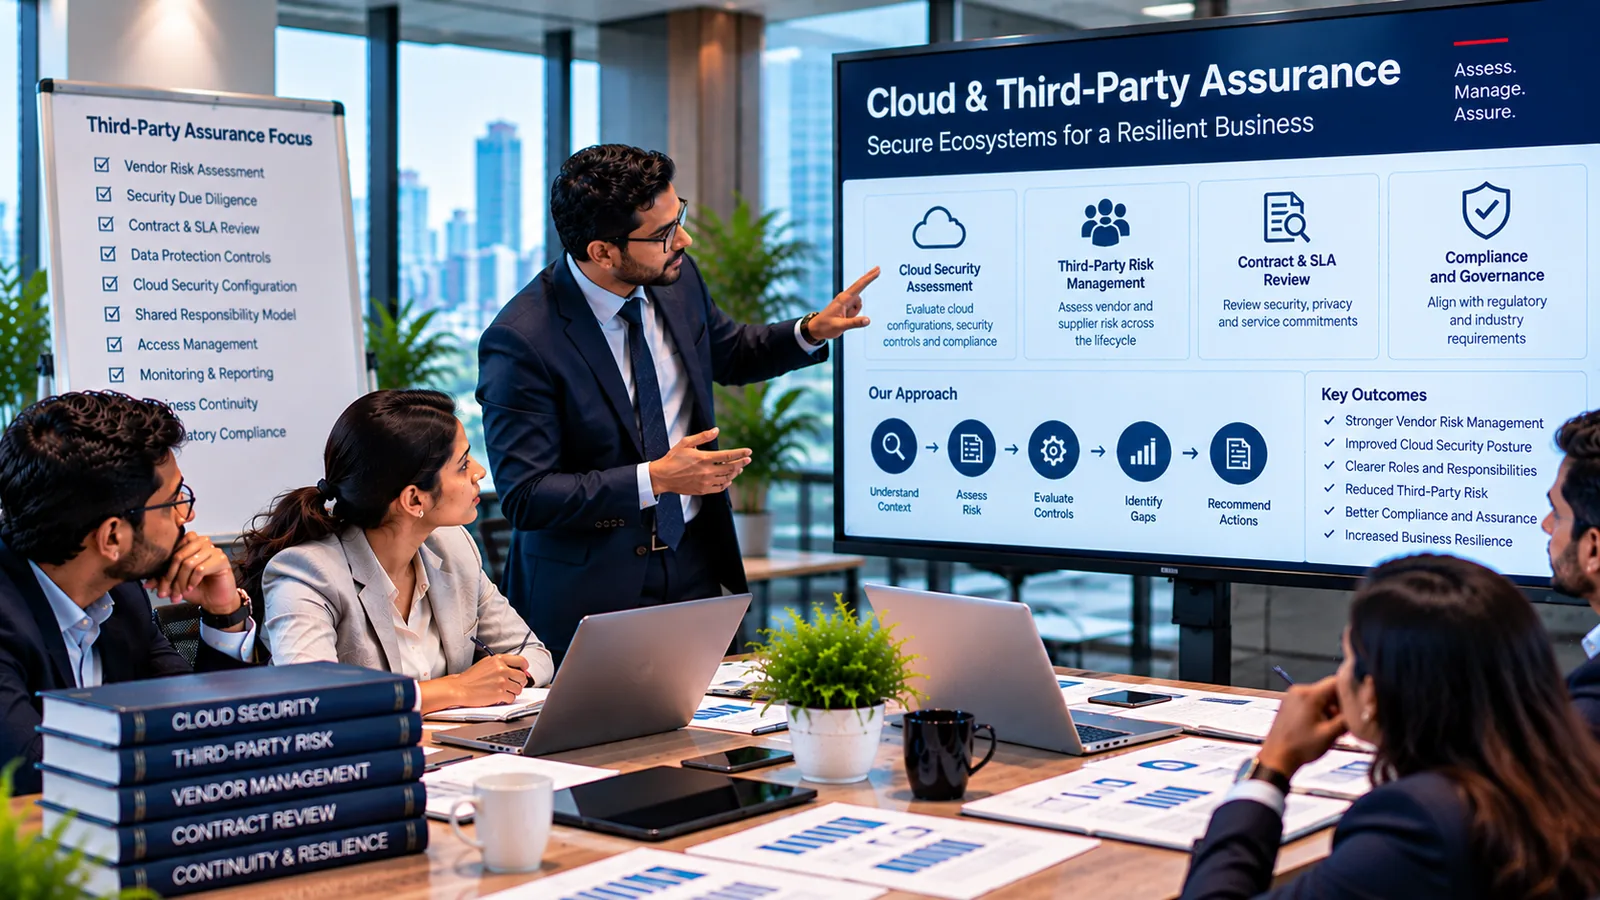
Assurance over the cloud you run on and the vendors you depend on.
Most of your sensitive data and critical processes now sit in cloud platforms and third-party services you don't fully control. We assess your cloud security posture and governance, clarify the shared-responsibility boundary, and run structured vendor and supply-chain risk assessments — so the risk you've outsourced is still the risk you can see.
Who this is for
Built for the people who answer for it.
Cloud-first organisations
Running critical workloads in AWS, Azure or GCP that need posture and governance assurance.
Risk and procurement teams
That must assess and monitor the security of a growing portfolio of vendors and suppliers.
Firms with supply-chain exposure
Whose resilience and compliance depend on the controls of parties further down the chain.
Business risks addressed
What this assessment helps you find.
- Cloud misconfigurations exposing data, identities or workloads.
- Assuming the cloud provider covers controls that are actually your responsibility.
- Vendors with access to your data and no evidence of their controls.
- Concentration and fourth-party risk hidden deeper in the supply chain.
- No ongoing visibility of vendor posture after onboarding.
Assessment objectives
What the engagement evaluates.
- Assess cloud security posture across configuration, identity and workloads.
- Review cloud governance and the shared-responsibility model.
- Evaluate vendor risk through structured due diligence.
- Assess supply-chain and concentration risk.
- Establish a repeatable approach to ongoing third-party monitoring.
Scope & control areas
What we review.
Cloud security
- Configuration and posture
- Identity and access
- Network and workload security
- Logging, monitoring and data protection
Cloud governance
- Shared-responsibility mapping
- Landing-zone and guardrails
- Cost/security policy as code
- Multi-cloud governance
Third-party risk
- Vendor inventory and tiering
- Security due diligence
- Contract and SLA review
- Ongoing monitoring and reassessment
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
Our approach
A practical, evidence-based method.
Map the estate
Inventory cloud accounts, critical workloads and the vendors with access to your data.
Assess cloud posture
Review configuration, identity and workload security against cloud control baselines.
Clarify responsibility
Map the shared-responsibility boundary so no control falls through the gap.
Assess vendors
Run structured security due diligence on tiered vendors and review contracts and SLAs.
Evaluate supply chain
Assess concentration, fourth-party and continuity risk across critical suppliers.
Report & monitor
Deliver findings and a practical model for ongoing third-party monitoring.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- Cloud account and workload inventory
- Cloud configuration and IAM exports
- Vendor inventory with data-access and criticality
- Vendor security questionnaires / certifications
- Key contracts, DPAs and SLAs (samples)
- Existing cloud and vendor risk assessments
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- Cloud security posture assessment
- Shared-responsibility mapping
- Vendor risk assessment and tiering
- Supply-chain and concentration risk view
- Risk-rated findings with evidence
- Remediation roadmap and monitoring model
Engagement options
Engage the way that fits.
Cloud posture assessment
A focused review of one or more cloud platforms' security and governance.
Third-party risk assessment
Structured due diligence across a defined set of vendors and suppliers.
Programme design
Design a repeatable cloud and third-party risk programme with ongoing monitoring.
Independence & scope of this service
This is an independent assessment and advisory engagement. It is not a penetration test of the cloud provider, not an audit of the vendor on the vendor's behalf, and not accredited certification. Where Srida IT implements cloud or vendor controls, any later assurance over them is performed by a separate team.
Related frameworks & standards
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your cloud & third-party assurance engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.