ISO & Frameworks · Audit & Assurance
AvailableKeep your management system audit-ready, all year
Internal audits that keep your ISO management system certification-ready.
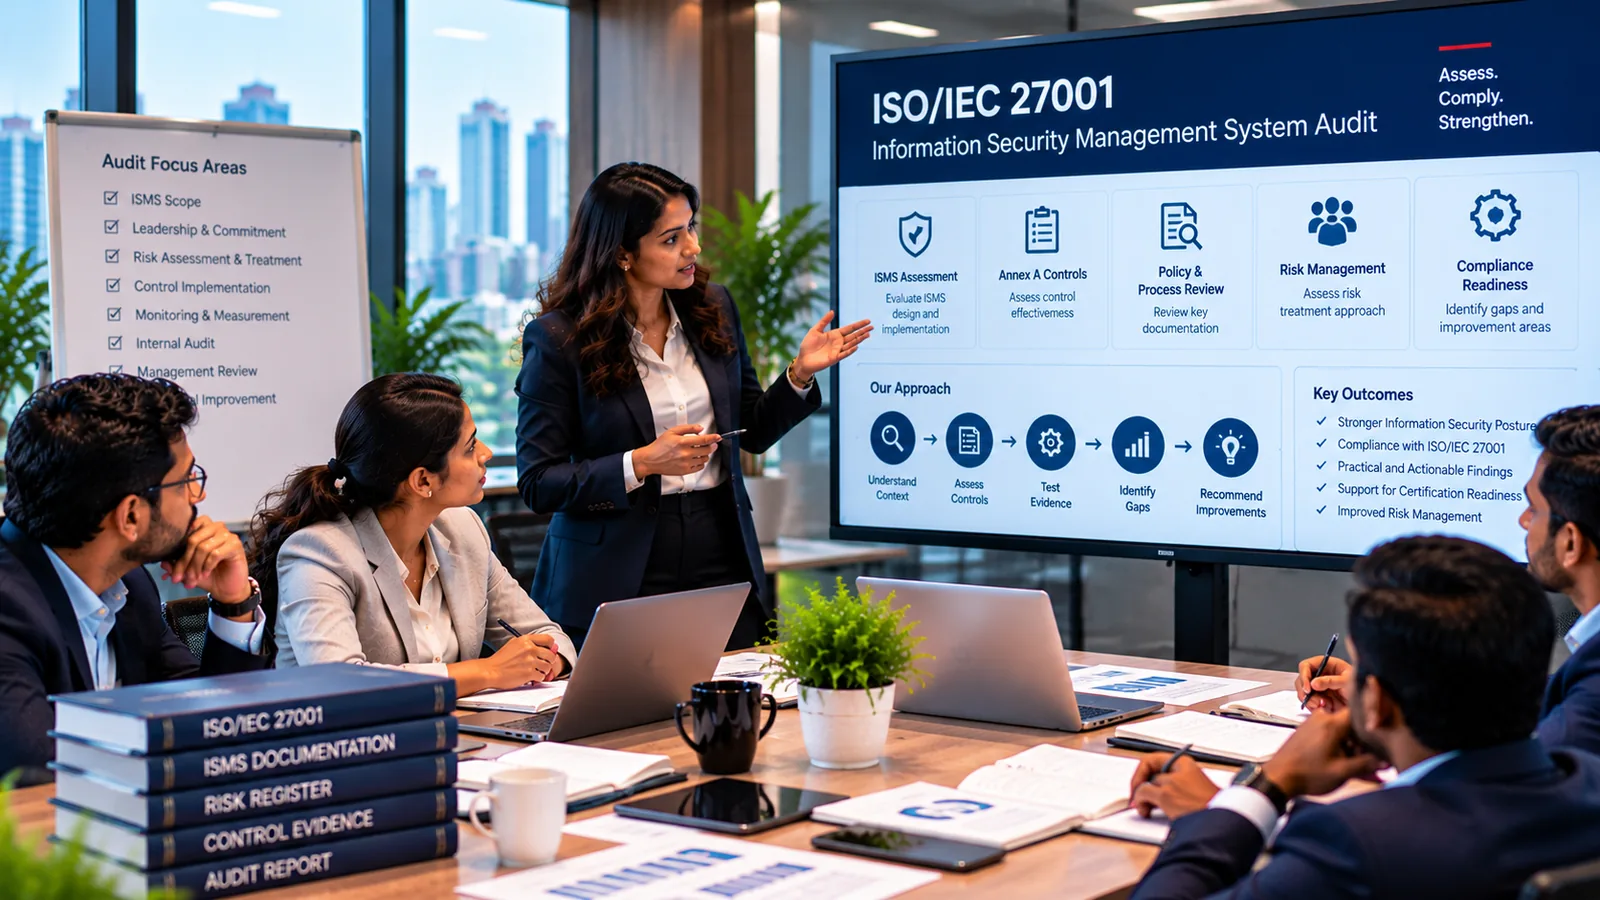
ISO management systems require independent internal audits — and they are often where certification is won or lost. We run clause-by-clause and control-level internal audits across ISO/IEC 27001, 42001, 27701, 22301 and 20000-1, support your management reviews, and track corrective actions to closure.
Who this is for
Built for the people who answer for it.
Organisations pursuing certification
That need a competent, independent internal audit before the certification body's stage 1 and stage 2 audits.
Already-certified organisations
That must sustain their management system and evidence internal audits at each surveillance cycle.
Teams without an internal auditor
Who need an impartial party to audit a system their own people built and operate.
Business risks addressed
What this assessment helps you find.
- Nonconformities discovered by the certification body that should have been caught internally.
- A management system that drifts out of conformity between surveillance audits.
- Internal audits performed by people auditing their own work — lacking independence.
- Corrective actions raised but never verified as effective.
- Management reviews that are not evidenced or not acted upon.
Assessment objectives
What the engagement evaluates.
- Assess conformity to the standard's clauses and applicable controls.
- Evaluate whether the management system is effectively implemented and maintained.
- Identify nonconformities and opportunities for improvement.
- Support management review with objective audit evidence.
- Track corrective actions through to verified closure.
Scope & control areas
What we review.
Management system clauses
- Context, leadership and planning
- Support and operation
- Performance evaluation
- Improvement and corrective action
Controls (standard-specific)
- ISO 27001 Annex A controls
- ISO 42001 AI management controls
- ISO 27701 privacy extension
- ISO 22301 continuity requirements
Programme health
- Risk assessment and treatment
- Internal audit and management review
- Documented information control
- Objectives and metrics
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
Our approach
A practical, evidence-based method.
Plan the audit
Agree the standard, scope, audit criteria and schedule, and build an audit plan and checklist.
Review documentation
Assess the management system documentation against the standard's requirements.
Audit on site / remote
Interview process owners and sample evidence to test conformity and effectiveness.
Raise findings
Document nonconformities (major/minor) and opportunities for improvement with evidence.
Support corrective action
Help define root-cause and corrective actions, and verify their effectiveness.
Feed management review
Provide objective audit results as an input to your management review.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- Management system scope and documentation
- Statement of Applicability and risk treatment plan (as applicable)
- Records of controls operating (samples)
- Previous internal/external audit results
- Management review records and objectives
- Corrective action and improvement logs
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- Internal audit plan and checklist
- Audit report with conformity assessment
- Nonconformities and observations with evidence
- Opportunities for improvement
- Corrective action tracker
- Management review input summary
Engagement options
Engage the way that fits.
Pre-certification internal audit
A full internal audit before your certification body's stage 1 / stage 2.
Surveillance-cycle internal audit
Recurring internal audits aligned to your certification surveillance schedule.
Multi-standard programme
A combined internal audit programme across several ISO management systems.
Independence & scope of this service
Srida IT performs independent internal audits. We are not an accredited certification body and we do not issue ISO certificates — accredited certification is granted only by an accredited certification body. Where we helped implement your management system, the internal audit is conducted by auditors independent of that implementation.
Related frameworks & standards
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your iso management system audits engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.