IT & Controls · Audit & Assurance
AvailableITGC and SOX readiness, done properly
Get your IT general controls audit-ready — before the auditors arrive.
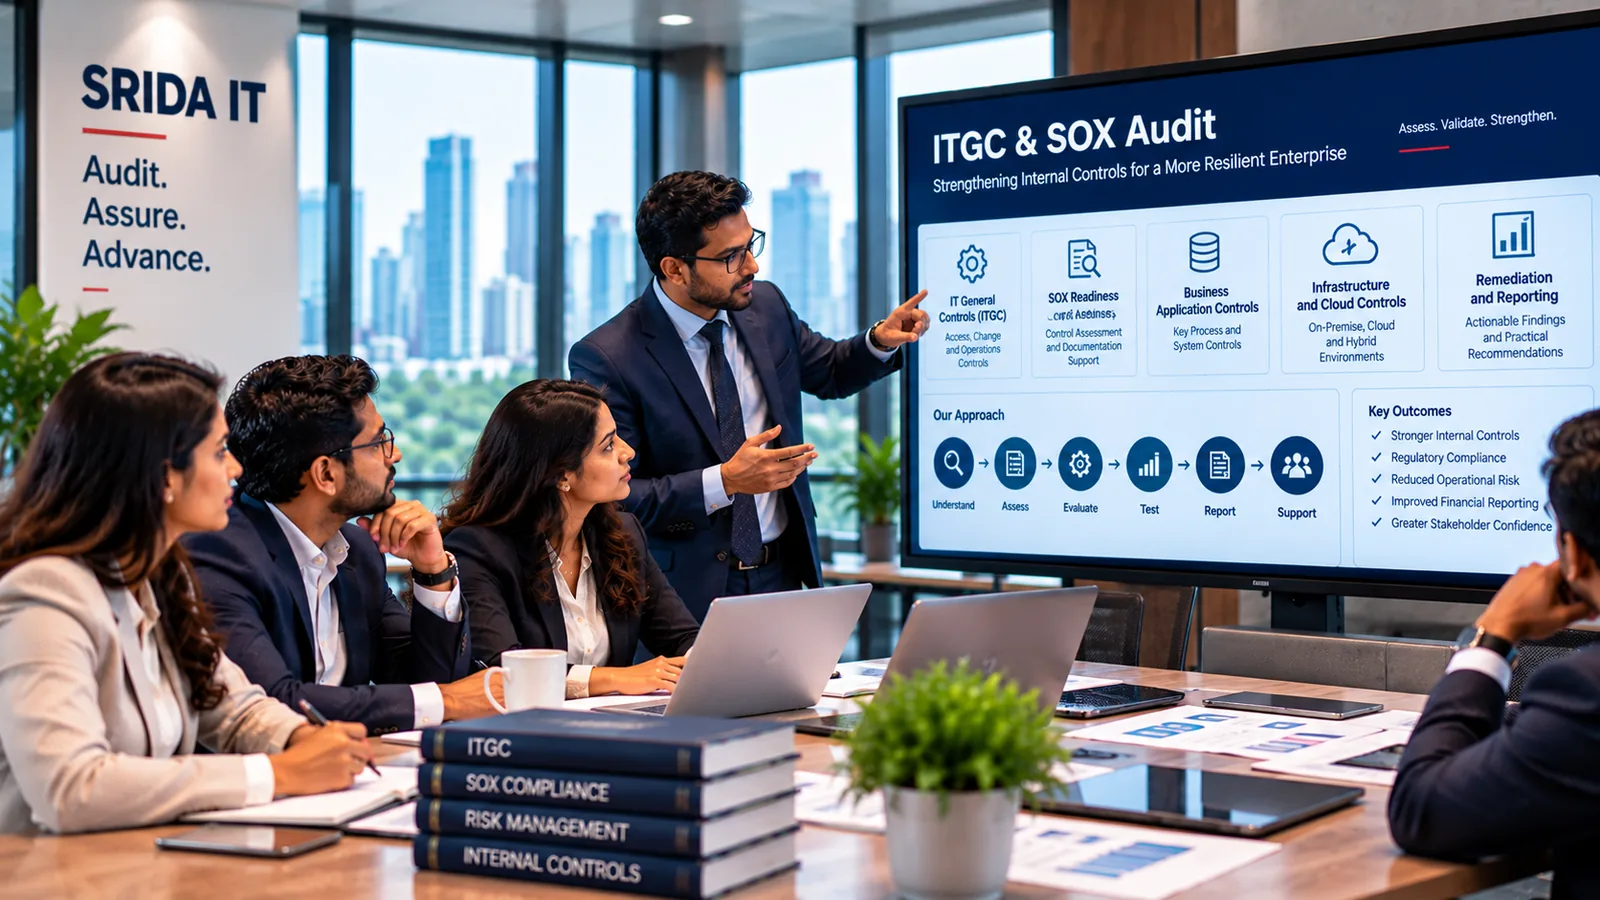
IT general controls sit underneath almost every financial and compliance assertion your organisation makes. We assess your logical access, change management, IT operations and application controls, prepare the evidence, and close the gaps — so your external auditors find a controlled environment, not surprises.
Who this is for
Built for the people who answer for it.
Finance & controllership teams
Preparing for SOX/ICFR or a financial statement audit who need the IT control layer to hold up.
IT & engineering leaders
Who own access, change and operations controls and need them evidenced and defensible.
Companies approaching a listing or raise
That need to demonstrate a mature, testable IT control environment to auditors and investors.
Business risks addressed
What this assessment helps you find.
- Access that is over-provisioned, unreviewed or not deprovisioned on exit.
- Changes promoted to production without authorisation, testing or segregation of duties.
- Control evidence that cannot be produced when the auditor asks for it.
- Application controls assumed to work but never validated.
- Audit findings and management letter points that could have been prevented.
Assessment objectives
What the engagement evaluates.
- Assess the design and operating effectiveness of ITGCs across key systems.
- Evaluate logical access, change management and IT operations controls.
- Review in-scope IT application controls supporting financial processes.
- Prepare and organise control evidence for external audit.
- Identify and remediate gaps ahead of the formal audit window.
Scope & control areas
What we review.
Logical access
- User provisioning and deprovisioning
- Privileged and emergency access
- Periodic access recertification
- Segregation of duties
Change management
- Change authorisation and approval
- Testing and segregation of duties
- Emergency change handling
- Release and deployment controls
IT operations
- Job scheduling and monitoring
- Backup and recovery
- Incident and problem management
- Data interface controls
Application controls
- Input / processing / output controls
- Automated calculations and validations
- Configurable control settings
- Key report integrity (IPE)
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
Our approach
A practical, evidence-based method.
Scope key systems
Identify the financially significant systems and the ITGCs and application controls that support them.
Walk through controls
Document each control, its owner and how it operates through walkthroughs and process mapping.
Test design & operation
Assess control design and test operating effectiveness across a defined sample and period.
Prepare evidence
Organise control evidence and information-produced-by-entity (IPE) into an audit-ready format.
Remediate gaps
Prioritise and support remediation of control gaps before the external audit begins.
Support the audit
Act as a knowledgeable liaison to coordinate with your external auditors during fieldwork.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- System and application inventory (financially significant)
- Access lists, role definitions and recertification records
- Change tickets, approvals and deployment logs (samples)
- Backup, job-scheduling and monitoring records
- Prior audit findings and management letters
- Policies and procedures for access, change and operations
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- ITGC and application control scope matrix
- Control walkthroughs and design assessment
- Operating effectiveness test results
- Gap analysis with risk ratings
- Audit-ready evidence pack
- Remediation roadmap with owners and timelines
- Management summary for finance and audit committee
Engagement options
Engage the way that fits.
Readiness assessment
A focused review to get ITGCs audit-ready before the external audit window.
Internal audit support
Co-source or support your internal audit function on the IT control plan.
Periodic review
Recurring ITGC testing aligned to your annual control calendar.
Independence & scope of this service
This is a readiness and internal-control assessment. It is not a statutory audit and does not express a statutory or SOX attestation opinion — those are issued by your external auditor. Where Srida IT helps remediate controls, the readiness assessment and any later assurance are kept separate to preserve independence.
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your itgc & sox readiness engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.