Mentorship by CISO · Hands-on GRC · 100% Remote
Practise GRC on real work.
A 12-week mentorship where you work through governance, risk and compliance tasks on simulated enterprise engagements — reviewed by a Top-50 CISO and an AI mentor, every step of the way.
First tracks live now: GRC 101 · GRC Analyst
Simulated enterprise work
You don't do toy exercises. Tasks are set on realistic engagements across IT, banking, healthcare and BPO — the way the work actually lands on a GRC analyst's desk.
Mentor feedback
Every activity is reviewed by a human CISO and an AI mentor — Socratic feedback that pushes you to defend your decisions, not just hand you the answer.
Standards-aligned
Everything you practise maps to the frameworks employers hire for: ISO/IEC 27001, NIST CSF 2.0, CIS Controls v8, SOC 2, GDPR and DPDPA.
Verifiable outcomes
Completed work becomes a CV of real engagements, credential badges for each skill, and a verifiable certificate anyone can check.
Your mentor
A Top-50 CISO reviews your work.
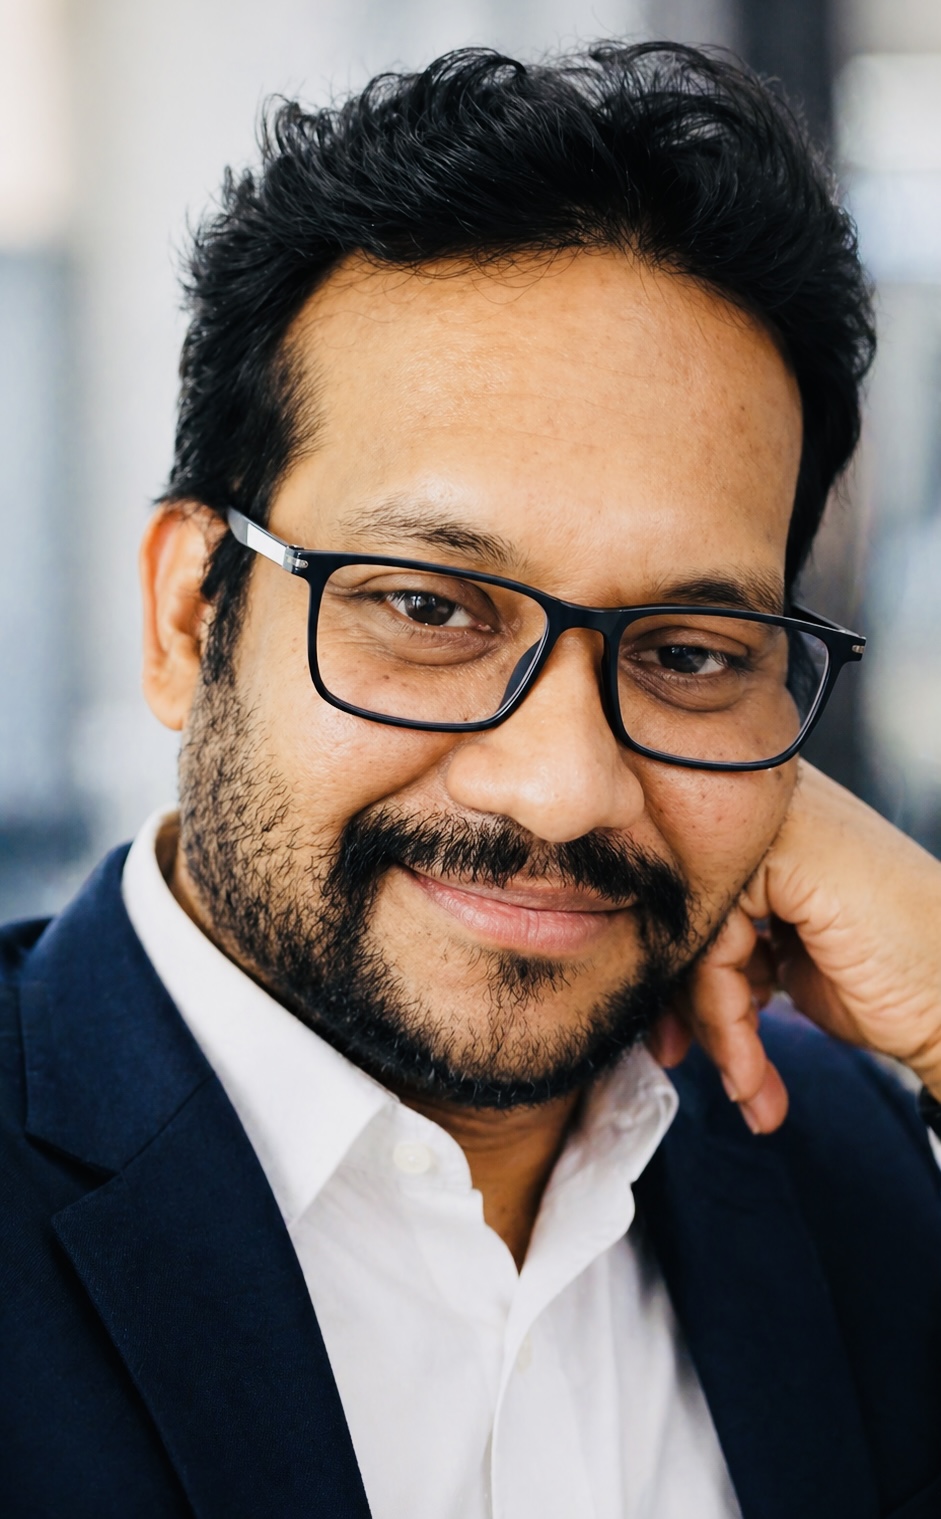
Rajendra Bodda
Top-50 CISO · Founder & CISO, Srida IT
This isn’t a course you watch — it’s your work, reviewed by a practising CISO. Rajendra has led independent audits, ISO/IEC 27001 ISMS implementations, SOC 2 readiness, AI governance and security programmes across BFSI, healthcare, manufacturing and technology. In the mentorship he sets the tasks, challenges your decisions, and holds your output to the bar an auditor or a board would.
Paired with an AI mentor for instant, Socratic feedback between reviews — so you’re never stuck waiting.
How it works
Real task → do the work → get mentored → earn the badge.
Pick a track
Start with GRC 101, or jump to a role track like GRC Analyst.
Get a real task
A task from a simulated enterprise engagement lands on your desk.
Do the work
Produce the actual artifact — a risk register, an SoA, an audit finding.
Get mentored
A CISO + AI mentor review it and challenge your decisions, Socratically.
Iterate to standard
Refine until it meets a professional bar you could defend in an audit.
Earn your badge
Bank a credential badge, add the work to your CV, and move on.
The tracks
Start at the foundation. Grow into a role.
Each track is a sequence of mentored, real-world tasks. Begin with GRC 101, then specialise. More tracks are added regularly.
GRC 101
Beginner
Governance, risk and compliance from the ground up — the language, the lifecycle, and your first real risk register.
GRC Analyst
Core
Operate as a GRC analyst: run risk assessments, map controls, collect evidence and support audits on simulated engagements.
ISMS Implementer — ISO/IEC 27001
Intermediate
Scope an ISMS, build the Statement of Applicability, and drive controls to audit-ready.
Risk Analyst
Intermediate
Quantify and treat risk, defend the numbers, and brief decision-makers.
IT / Security Auditor
Intermediate
Plan an audit, test controls, sample evidence, and write findings to professional standard.
Privacy / DPO
Intermediate
Data mapping, DPIAs and DPDPA/GDPR obligations on real-world data flows.
Standards-aligned
Everything maps to what employers hire for.
What you walk away with
Proof, not just a certificate.
A CV of real work
Every task you complete is portfolio evidence — not a certificate of attendance.
Credential badges
Earn a verifiable badge for each skill and track you complete.
A verifiable certificate
Issued by Srida IT Academy and checkable at sridait.com/verify-certificate.
Who it's for
For anyone who learns by doing.
Learn GRC the way the job actually works.
12 weeks, 100% remote, mentored by a Top-50 CISO. Start with GRC 101 and build a portfolio of real work.