Readiness · Audit & Assurance
AvailableWalk into your SOC examination prepared
Be ready for your SOC examination — before the CPA firm starts.
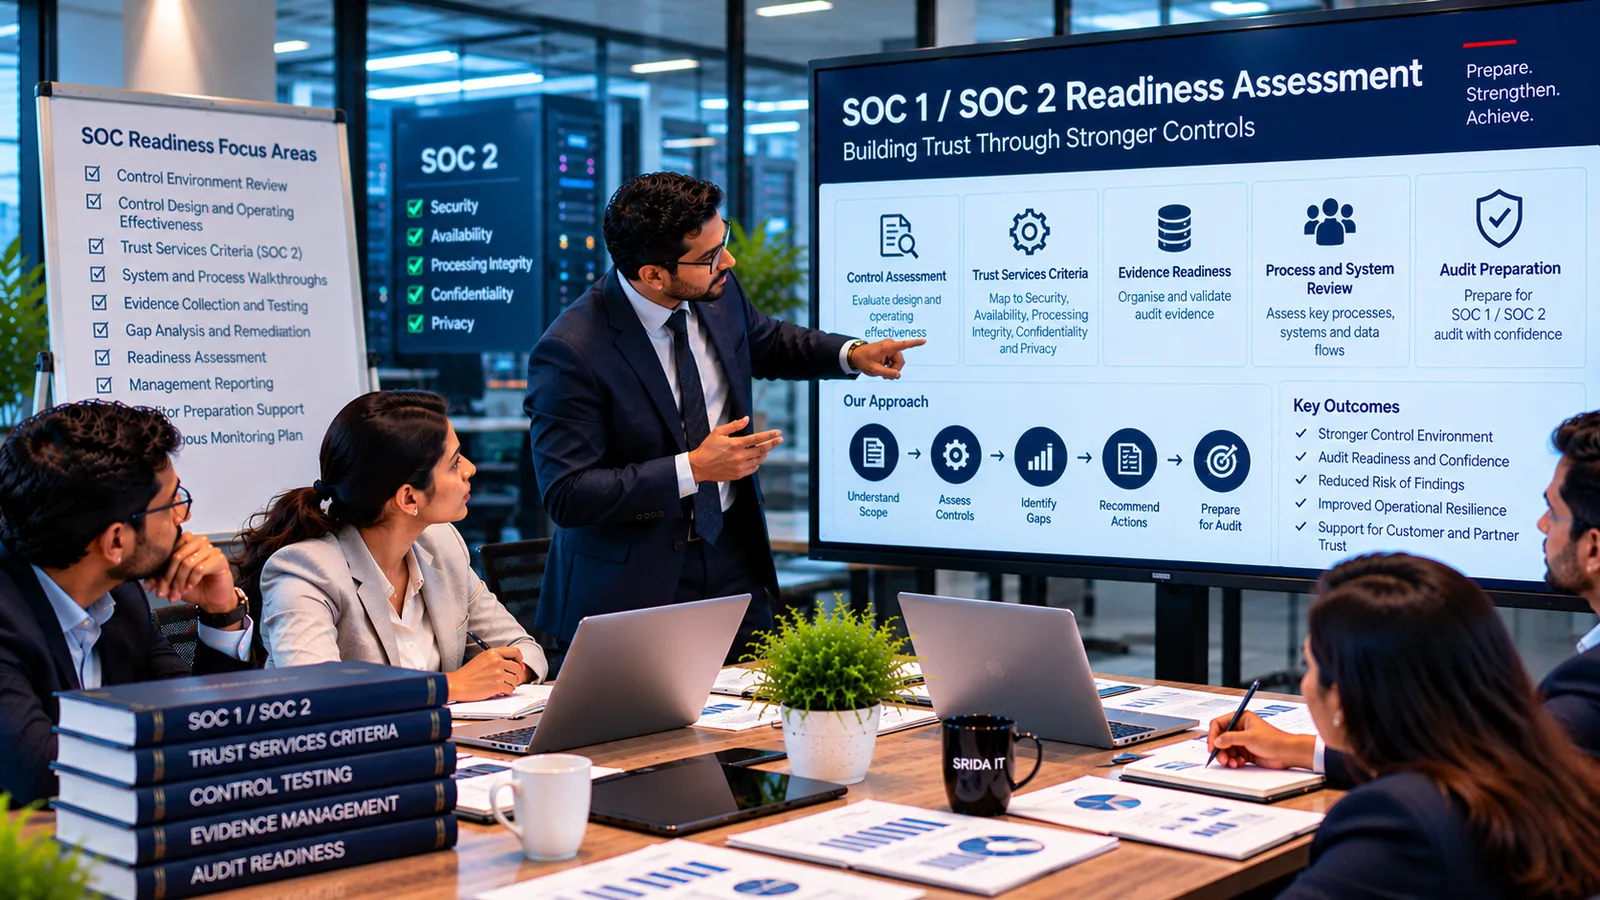
A SOC examination is only as smooth as the preparation behind it. We map your controls to the Trust Services Criteria, find the gaps, help you build the evidence and remediate — then coordinate with your CPA/attestation firm so the formal examination has no surprises.
Who this is for
Built for the people who answer for it.
SaaS and service providers
Whose enterprise customers require a SOC 2 report before they will buy or renew.
Organisations facing a first SOC
That have never been through an examination and need a clear, de-risked path to the report.
Teams between report cycles
That need to keep controls operating and evidence fresh ahead of the next Type II period.
Business risks addressed
What this assessment helps you find.
- Entering a formal examination unprepared and receiving qualified findings.
- Controls that do not map cleanly to the Trust Services Criteria in scope.
- Evidence that is incomplete, inconsistent or cannot be produced for the period.
- A Type II observation window that starts before controls are actually operating.
- Wasted examination fees re-running work that readiness would have caught.
Assessment objectives
What the engagement evaluates.
- Confirm the right report (SOC 1 vs SOC 2) and Trust Services Criteria in scope.
- Map existing controls to the criteria and identify gaps.
- Prepare and organise the evidence the examiner will request.
- Remediate gaps before the examination (or Type II observation) begins.
- Coordinate a smooth handover to your attestation firm.
Scope & control areas
What we review.
Scoping
- SOC 1 vs SOC 2 determination
- Trust Services Criteria selection
- System description boundaries
- Type I vs Type II planning
Control areas
- Security (common criteria)
- Availability
- Confidentiality
- Processing integrity and privacy (as selected)
Readiness
- Control gap analysis
- Evidence design and collection
- Remediation planning
- Examiner coordination
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
Our approach
A practical, evidence-based method.
Scope the report
Determine SOC 1 vs SOC 2, the criteria in scope and the system description boundaries.
Map controls
Map your existing controls to each criterion and identify where coverage is missing or weak.
Assess gaps
Evaluate design and readiness of each control and risk-rate the gaps to close.
Build evidence
Design the evidence each control needs and help you collect it consistently for the period.
Remediate
Prioritise and support remediation so controls are operating before the observation window.
Coordinate the examination
Hand over to your CPA/attestation firm and support them through fieldwork.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- Draft system description and architecture
- Existing control documentation and policies
- Access, change and monitoring records (samples)
- Vendor and subservice organisation list
- Prior SOC reports or readiness results (if any)
- HR, onboarding and offboarding records (samples)
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- Scope and criteria determination
- Controls-to-criteria mapping
- Gap analysis with risk ratings
- Evidence design and collection plan
- Remediation roadmap
- Examination readiness summary and auditor-coordination support
Engagement options
Engage the way that fits.
Readiness assessment
A full gap analysis and evidence-preparation engagement before the examination.
Type II preparation
Preparation specifically for a Type II observation period, including evidence cadence.
Periodic readiness
Recurring readiness between report cycles to keep controls and evidence current.
Independence & scope of this service
Srida IT provides SOC readiness. We do not issue SOC reports — a SOC examination and report (Type I or Type II) is performed and signed only by a licensed CPA / attestation firm. We prepare you for that examination and coordinate with your chosen firm; where we remediate controls, independence from any later assurance is preserved.
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your soc 1 / soc 2 readiness engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.