Global Compliance Library
European Union
GDPR, DORA, NIS2 and the EU AI Act.
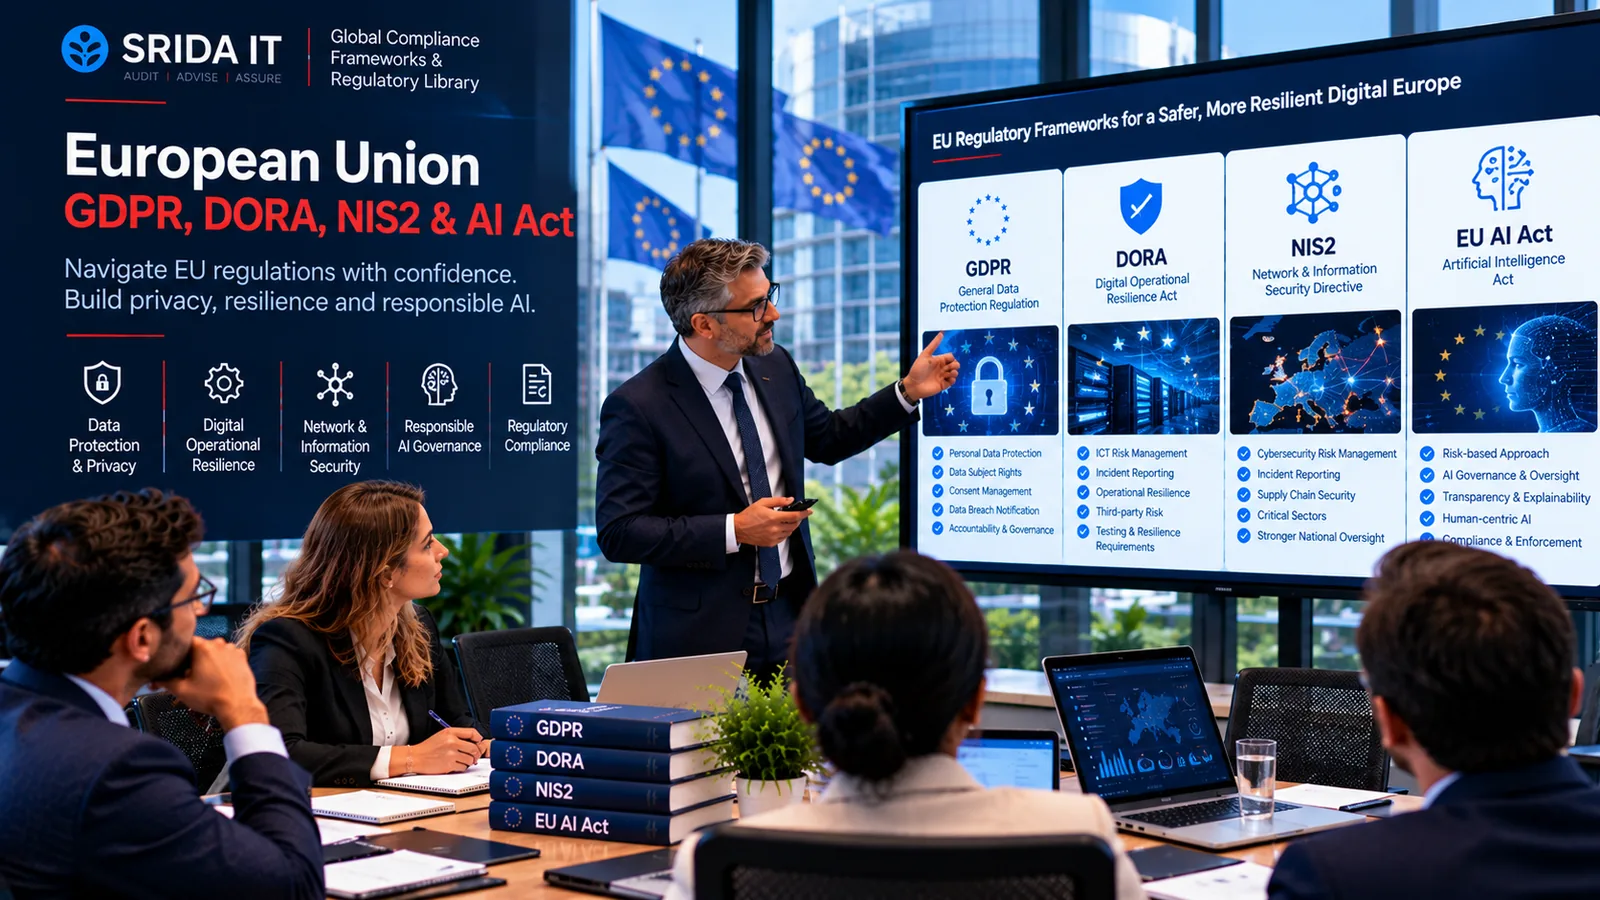
GDPR
ConditionalGeneral Data Protection Regulation
Regulation
- Authority:
- European Union (Regulation (EU) 2016/679)
- Status:
- In force
- Applies to:
- Controllers/processors in the EU, and those outside the EU offering goods/services to, or monitoring, people in the EU.
DORA
MandatoryDigital Operational Resilience Act
Regulation
- Authority:
- European Union (Regulation (EU) 2022/2554)
- Status:
- In force / applies
- Applies to:
- A broad range of EU financial entities and their critical ICT third-party providers.
NIS2
MandatoryNIS2 Directive
Directive
- Authority:
- European Union (Directive (EU) 2022/2555)
- Status:
- In force; transposed into national law (dates vary by member state)
- Applies to:
- 'Essential' and 'important' entities in listed sectors — exact obligations arise under each member state's implementing law.
EU AI Act
ConditionalEU Artificial Intelligence Act
Regulation
- Authority:
- European Union (Regulation (EU) 2024/1689)
- Status:
- In force; obligations apply in phases
- Applies to:
- Providers and deployers of AI systems placed on the EU market or affecting people in the EU, on a risk-based basis.
This library provides general information for orientation only. It is not legal advice, a determination of applicability, or a substitute for formal certification or professional counsel. Verify current legal status, editions and dates against the official source before relying on any entry. Inclusion of a jurisdiction or instrument here is informational and does not imply that Srida IT provides regulated services, holds local authorisation, or has a presence in that jurisdiction.