OT & Industrial · Audit & Assurance
Specialist · On requestProtect operations without disrupting them
Secure the systems that run the physical world — safely.
Industrial and operational technology was built for safety and uptime, not for today's threats. We assess OT security governance, industrial network architecture and ICS/SCADA risk — using a safe, non-intrusive methodology aligned to IEC 62443 — so you strengthen security without ever putting live operations at risk.
Who this is for
Built for the people who answer for it.
Manufacturing & industrial firms
Running ICS/SCADA and OT environments that are increasingly connected and exposed.
Critical infrastructure operators
With safety-critical operations and regulatory expectations for OT security.
IT/OT convergence teams
Bridging enterprise IT and plant-floor OT who need a clear, safe risk picture.
Business risks addressed
What this assessment helps you find.
- Flat networks where IT and OT are not segmented, letting threats cross over.
- Unknown or unmanaged OT assets with no inventory.
- Legacy ICS/SCADA that cannot be patched and has weak access controls.
- Remote access to OT without adequate controls or monitoring.
- Security testing that, done wrong, could disrupt safety-critical operations.
Assessment objectives
What the engagement evaluates.
- Assess OT security governance and ownership.
- Build or validate the OT asset inventory.
- Review industrial network architecture and segmentation.
- Assess ICS/SCADA access, monitoring and remote-access controls.
- Identify risks against IEC 62443 using a safe, non-intrusive approach.
Scope & control areas
What we review.
OT governance
- OT security policy and ownership
- IT/OT convergence governance
- Vendor and integrator management
- Safety and security alignment
Assets & network
- OT asset inventory
- Network architecture and zones
- Segmentation and conduits (IEC 62443)
- Remote access to OT
Monitoring & response
- OT logging and monitoring
- Access and authentication controls
- Patch and vulnerability handling
- OT incident response readiness
Audit criteria & frameworks
We confirm the applicable standards and editions during scoping. Framework names are used to describe audit criteria and do not imply accredited certification authority.
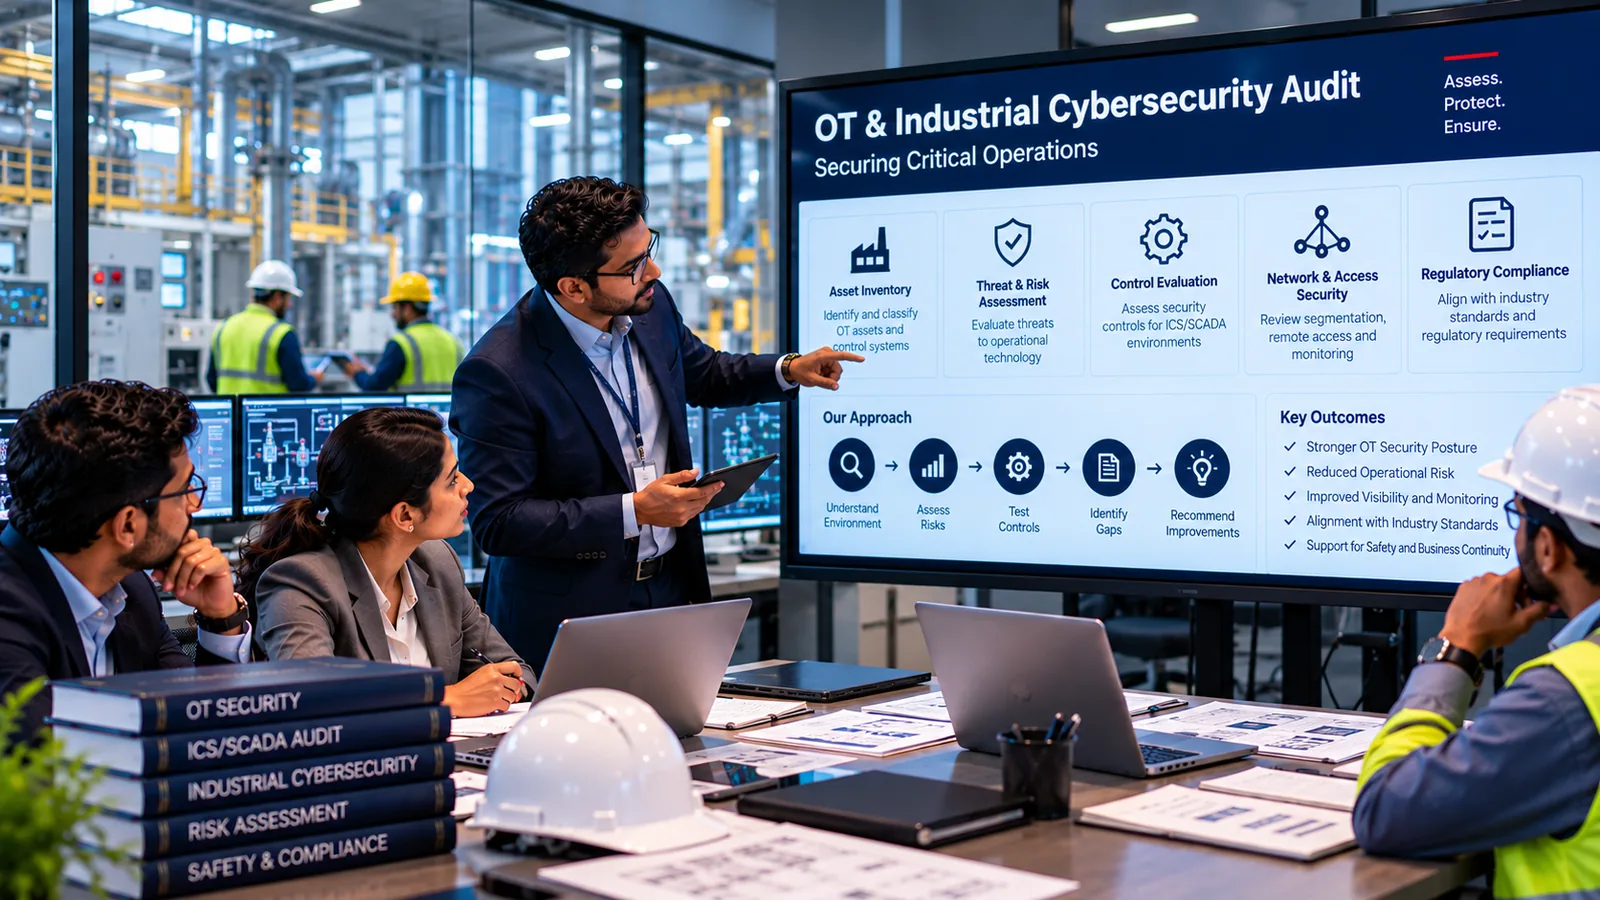
Our approach
A practical, evidence-based method.
Understand the environment
Work with your OT and safety teams to understand the plant, processes and constraints — safety first.
Inventory assets
Build or validate the OT asset inventory using passive, non-intrusive methods.
Review architecture
Assess network architecture, zones and conduits, and IT/OT segmentation against IEC 62443.
Assess controls
Review access, remote access, monitoring and patch handling for OT and ICS/SCADA.
Risk-rate findings
Rate risks with operational and safety impact in mind, not just IT severity.
Report & roadmap
Deliver findings against IEC 62443 and a prioritised, operationally realistic roadmap.
Evidence & client prerequisites
What we typically ask for.
Indicative only — the exact evidence depends on scope. Not every engagement requires every item.
- OT asset and system documentation
- Network diagrams and segmentation design
- Remote-access and vendor-access arrangements
- OT policies and procedures
- Monitoring and logging configuration (where present)
- Prior OT assessments or incidents
Deliverables
What you receive.
We only promise deliverables appropriate to this service and the agreed scope.
- OT security governance assessment
- OT asset inventory (built or validated)
- Network architecture and segmentation review
- ICS/SCADA controls assessment
- Risk-rated findings with safety-aware prioritisation
- IEC 62443-aligned improvement roadmap
Engagement options
Engage the way that fits.
OT risk assessment
A safe, non-intrusive assessment of OT security governance, architecture and controls.
Segmentation review
A focused review of IT/OT segmentation and network zones/conduits.
OT programme design
Help design an OT security programme aligned to IEC 62443.
Independence & scope of this service
This is a specialist engagement scoped on request. We use a safe, non-intrusive methodology — we do not perform intrusive or active testing of live industrial environments without an explicitly agreed, safe testing methodology and your authorisation. This is an assessment, not accredited certification.
Related services
Related products
Learn more
Frequently asked questions
Practical answers.
Ready to scope your ot / industrial cybersecurity engagement?
A partner reviews every request and replies within one working day. Tell us your context and we’ll propose a right-sized scope.