Global Compliance Library
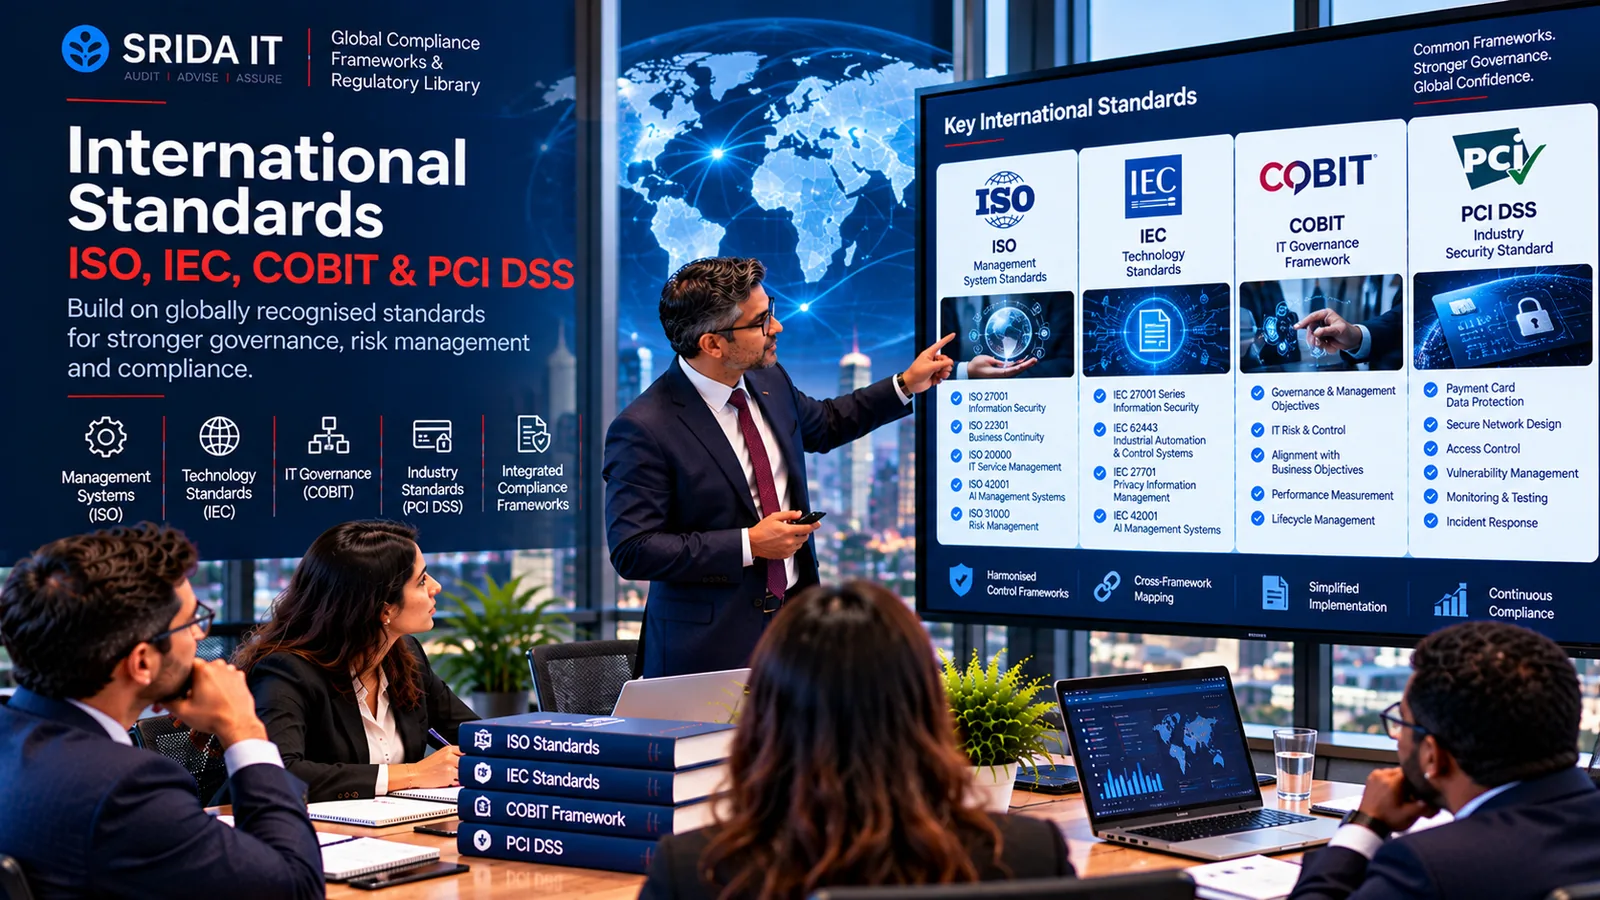
International Standards
ISO/IEC, NIST, COBIT, COSO, CIS, PCI DSS and SOC.
ISO 27001
VoluntaryISO/IEC 27001
Management system standard
- Authority:
- ISO / IEC
- Status:
- Current edition: ISO/IEC 27001:2022
- Applies to:
- Any organisation seeking to manage information security through a certifiable management system.
ISO 42001
VoluntaryISO/IEC 42001
Management system standard
- Authority:
- ISO / IEC
- Status:
- Current edition: ISO/IEC 42001:2023
- Applies to:
- Organisations that develop, provide or use AI systems and want a certifiable AI management system.
ISO 27701
VoluntaryISO/IEC 27701
Management system standard
- Authority:
- ISO / IEC
- Status:
- Current edition: ISO/IEC 27701:2019 (extension to 27001)
- Applies to:
- Organisations operating an ISMS that want to extend it to a privacy information management system (PIMS).
ISO 22301
VoluntaryManagement system standard
- Authority:
- ISO
- Status:
- Current edition: ISO 22301:2019
- Applies to:
- Organisations that need a business continuity management system (BCMS).
ISO 31000
VoluntaryVoluntary standard
- Authority:
- ISO
- Status:
- Current edition: ISO 31000:2018 (guidance, not certifiable)
- Applies to:
- Any organisation seeking principles and guidelines for risk management.
NIST CSF
VoluntaryNIST Cybersecurity Framework
Control framework
- Authority:
- US National Institute of Standards and Technology (NIST)
- Status:
- Current edition: CSF 2.0
- Applies to:
- Voluntary framework used worldwide to manage cybersecurity risk (adds the 'Govern' function in 2.0).
NIST AI RMF
VoluntaryNIST AI Risk Management Framework
Control framework
- Authority:
- US National Institute of Standards and Technology (NIST)
- Status:
- AI RMF 1.0 (with Generative AI Profile companion)
- Applies to:
- Voluntary framework for organisations designing, developing, deploying or using AI systems.
SP 800-53
MandatoryNIST SP 800-53
Control framework
- Authority:
- US National Institute of Standards and Technology (NIST)
- Status:
- Revision 5 (with ongoing release updates)
- Applies to:
- US federal information systems; widely adopted as a control catalogue by others.
CIS Controls
VoluntaryCIS Critical Security Controls
Control framework
- Authority:
- Center for Internet Security (CIS)
- Status:
- CIS Controls v8.1
- Applies to:
- Any organisation seeking a prioritised set of defensive actions (Implementation Groups 1-3).
COBIT
VoluntaryGovernance framework
- Authority:
- ISACA
- Status:
- COBIT 2019
- Applies to:
- Enterprises governing and managing information and technology; often used in ITGC/SOX contexts.
COSO ICIF
VoluntaryCOSO Internal Control – Integrated Framework
Control framework
- Authority:
- Committee of Sponsoring Organizations of the Treadway Commission (COSO)
- Status:
- 2013 Framework
- Applies to:
- Organisations designing internal control; the standard reference for SOX/ICFR.
PCI DSS
ContractualIndustry security standard
- Authority:
- PCI Security Standards Council
- Status:
- Current version: 4.0.1
- Applies to:
- Entities that store, process or transmit cardholder data; enforced contractually by payment brands.
SOC 2
ContractualAssurance / attestation criteria
- Authority:
- AICPA (Trust Services Criteria; SSAE 18 attestation standards)
- Status:
- Trust Services Criteria (2017, revised 2022)
- Applies to:
- Service organisations whose customers require assurance over security and related criteria. A SOC 2 report is issued only by a licensed CPA firm.
SOC 1
ContractualAssurance / attestation criteria
- Authority:
- AICPA (SSAE 18, AT-C 320)
- Status:
- SSAE 18 attestation standards
- Applies to:
- Service organisations whose controls are relevant to their clients' financial reporting (ICFR). Issued only by a licensed CPA firm.
This library provides general information for orientation only. It is not legal advice, a determination of applicability, or a substitute for formal certification or professional counsel. Verify current legal status, editions and dates against the official source before relying on any entry. Inclusion of a jurisdiction or instrument here is informational and does not imply that Srida IT provides regulated services, holds local authorisation, or has a presence in that jurisdiction.